HIPAA
Learn about Softlinx’s HIPAA-compliant faxing solutions for secure, efficient, and regulatory-approved document communication.
HIPAA Rules for Faxing Medical Records: What Healthcare Teams Must Know in 2025
HIPAA rules for faxing medical records still apply to a majority of U.S. hospitals and clinics that rely on fax for referrals, authorizations, lab reports, and release of information requests. Three federal rules control every faxed document that contains PHI: the HIPAA Privacy Rule, the HIPAA Security Rule, and the Breach Notification Rule. Those rules also shape the first page of every transmission, which is why HIPAA-compliant fax cover sheets carry the confidentiality notice, recipient details, and misdirection instructions auditors expect to see.
These rules decide when a provider may send patient medical records by fax, who may receive them, how they must be protected, and what happens when a fax reaches the wrong recipient. Beyond the specific record types, the importance of HIPAA-compliant faxing comes down to protecting PHI at every step of transmission, from sender authentication to confirmation logs.
The Privacy Rule defines lawful use and disclosure of PHI. The Security Rule requires safeguards for electronic faxes and stored images, including authentication, access limits, and, where reasonable and appropriate, encryption.
The Breach Notification Rule dictates the steps a covered entity must take when PHI reaches an unauthorized person. Fax remains legal under HIPAA, but only when HIPAA rules for faxing medical records shape every part of the workflow.
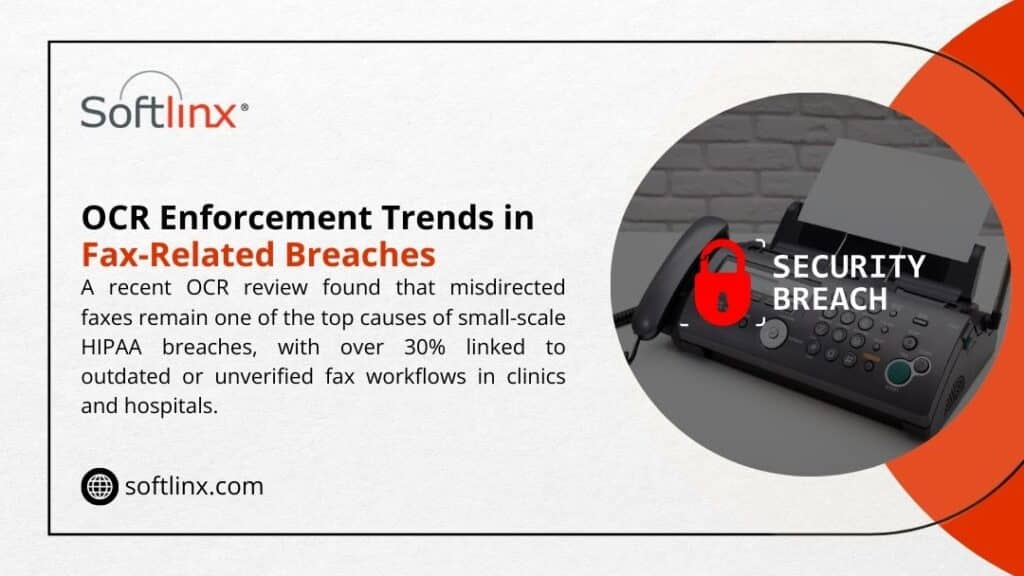
Fax-related incidents continue to appear in OCR investigations, especially when devices are unsecured or numbers are misdialed, which shows these risks are still very real.
Healthcare organizations close most of these risks through modern HIPAA-compliant cloud fax with verified fax numbers, access control, audit trails, and controlled routing into an EHR.
Softlinx builds its secure cloud fax platform around these requirements so hospitals, clinics, and specialty practices follow HIPAA rules for faxing medical records without slowing down clinical tasks.
Why HIPAA rules for faxing medical records still matter in 2025
Fax never fully left healthcare. Surveys and industry reports show that a large portion of hospitals and physician groups still depend on fax for coordination with external partners, payers, and pharmacies.
At the same time, regulators now look harder at data security and access rights than at any previous point. The HIPAA Privacy Rule still grants patients a clear right of access to medical records, while the Security Rule and new enforcement pressure focus on gaps that lead to breaches.
That context places HIPAA rules for faxing medical records in a tight spotlight:
- A misdirected fax with PHI can count as a HIPAA breach and trigger breach notification duties.
- A slow or clumsy fax workflow can interfere with a patient’s right to receive copies of records within the time frames set in 45 CFR 164.524.
- Old fax machines that sit in public areas weaken physical safeguards that the HIPAA Security Rule expects from covered entities.
Cloud fax and electronic health records (EHR) have not erased fax numbers from referral forms. Instead, HIPAA rules for faxing medical records push health systems toward secure Healthcare Fax Solutions that align with the Privacy Rule, Security Rule, and Breach Notification Rule without forcing staff to abandon familiar fax workflows.
workflows.
Can you fax medical records under HIPAA?
Yes. HIPAA allows fax transmission of PHI such as lab reports, consult notes, and discharge summaries, as long as covered entities use reasonable safeguards. The Office for Civil Rights (OCR) states that a physician may fax patient medical information to another provider for treatment purposes and may disclose PHI by fax for other standard HIPAA use cases.
The key question is not “fax or no fax,” but “do current processes match HIPAA rules for faxing medical records when those records leave your system?”
The main HIPAA rules for faxing medical records sit in three pillars:
In short, HIPAA rules for faxing medical records do not ban fax machines, but they treat any faxed document that contains PHI as part of the same regulatory framework that covers EHR entries and other digital medical records. For deeper policy detail, Softlinx already covers the high-level questions around HIPAA fax and common myths about HIPAA-compliant fax workflows.
Core HIPAA rules for faxing medical records in daily operations
When a nurse, registrar, or medical records clerk presses “send,” several specific risks and safeguards come into play. OCR expects covered entities to prevent unauthorized access in ways that match the size and complexity of each organization.
The table below condenses how HIPAA rules for faxing medical records map to concrete actions.
| Risk area | What HIPAA expects | Example of better practice with secure fax |
| Wrong fax number | Reasonable steps to verify recipient identity and contact details before disclosure of PHI. | Staff confirm the fax number in the EHR or scheduling system, then select it from a verified list inside a HIPAA-compliant fax solution instead of dialing digits on a physical fax machine keypad. |
| Unnecessary PHI on the fax | Minimum necessary use and disclosure under the Privacy Rule. | HIPAA rules for faxing medical records favor concise packets: only the pages that relate to the clinical question or claim review, not the entire designated record set. |
| PHI seen in a public area | Physical safeguards under the Security Rule, plus Privacy Rule expectations around incidental disclosure. | Fax delivery moves to a secure cloud fax portal with user logins, rather than a hallway fax tray. If a multi-function device still receives paper, it sits in a restricted office, not a lobby. |
| Weak access control for electronic faxes | Technical safeguards such as unique user IDs, role-based access, and access logging. | Electronic faxes sit inside a cloud fax service that ties into single sign-on, logs every view and download, and limits PHI access to staff whose roles fit that patient’s care or billing work. |
| No fax cover sheet or weak warnings | Reasonable safeguards, plus OCR guidance on limiting disclosure to intended recipients. | Every fax that carries PHI uses a fax cover sheet template with a strong confidentiality notice, sender and recipient details, and a request to destroy misdirected faxes. |
| No audit trail | Documentation requirements for HIPAA compliance and breach investigation. | The fax system keeps a durable log: date, time, fax number, user ID, and delivery status for each faxed document. In a cloud fax portal, staff can export this log during an audit. |
These safeguards sit at the heart of HIPAA rules for faxing medical records. They protect protected health information (PHI) at each stage: creation, transmission, receipt, storage, and disposal.
Providers that still rely on analog devices can reach part of that standard, but secure cloud fax platforms give far stronger control over PHI in healthcare while still allowing staff to send faxes with a familiar workflow.
If your team still depends on legacy telephony, Softlinx explains how modern fax through the internet resolves many of those exposure points without ripping out every existing process.
What are the minimum safeguards for a HIPAA compliant fax?
AI overviews and PAA boxes tend to spotlight a simple version of this question. The short answer: HIPAA rules for faxing medical records expect a mix of policy, training, and technical safeguards that cover both paper faxes and electronic faxes.
Cloud fax services that Softlinx describes as HIPAA-compliant fax wrap these safeguards into a managed platform. That framework reduces the chance that one missed step by front-line staff turns a simple fax into a HIPAA violation.
How HIPAA rules for faxing medical records affect different care settings
Compliance risk shifts slightly from one setting to another, but HIPAA rules for faxing medical records set the same core obligations for every covered entity. The table below illustrates how common care environments face specific fax risks and how targeted cloud fax solutions help.
| Care setting | Typical fax use | Key HIPAA risk | Cloud fax angle |
| Acute-care hospital | Discharge summaries, transfer packets, referrals, and payer authorizations. | High fax volume makes it easy for patient information to reach the wrong floor or external number. | A hospital cloud fax solution routes inbound faxes directly into the EHR or secure folders and ties each faxed document to the right medical record number. |
| Community clinic | Specialty referrals, charity care documents, and release of medical records. | Shared devices and small spaces make paper faxes visible to visitors. | A clinic cloud fax solution replaces paper trays with inboxes inside a secure web portal that staff reach with unique logins. |
| Urgent care center | Work notes, test results, referrals to primary care. | Fast pace tempts staff to shortcut verification of fax numbers. | An urgent care cloud fax solution lets staff pick recipients from verified directories instead of keying in full fax numbers at speed. |
| Dental and specialty practices | Treatment notes, pre-authorizations, images, or reports. | Many practices sit outside hospital IT and may not have mature HIPAA safeguards for fax devices. | A dental office cloud fax solution or other specialty package adds HIPAA compliance without the cost of a full in-house infrastructure. |
Softlinx publishes separate guidance for hospital, clinic, and other specialty cloud fax solutions, which helps each practice map HIPAA rules for faxing medical records to its own scale and workflow mix.
How HIPAA rules for faxing medical records intersect with the right of access and release of information
HIPAA does more than restrict disclosure; it also gives patients a clear set of rights. The Privacy Rule grants patients the right to access, inspect, and receive a copy of medical records from covered entities, with only limited exceptions and with time limits that appear in 45 CFR 164.524.
Fax still plays a role in those rights:
| Patient-centered issue | Relevance of HIPAA rules for faxing medical records |
| Right of access | Many patients ask, “How can I get my medical records fast?” HIPAA allows providers to send copies by fax if the patient requests that method and accepts related risks. Staff must confirm the fax number, document the request, and send only the PHI the patient has requested. |
| “Who can access my medical records without my permission?” | HIPAA laws permit certain disclosures without explicit authorization, such as treatment, payment, health care operations, and specific public health or law-enforcement scenarios. The same rules apply when PHI travels by fax, so any such fax requires the same minimum necessary standard and safeguards. |
| Release of information to third parties | An attorney’s request on HIPAA rules for faxing medical records, an employer’s request, or a life-insurance request usually needs a signed HIPAA authorization or HIPAA medical release form. Fax remains a common channel here, but the presence of that HIPAA release form does not excuse poor security practices. |
| Access to digital medical records | Many systems route faxed documents into an electronic health record, where they become part of the designated record set. Patients then exercise HIPAA rights through patient portals and other digital means. |
Because faxed medical records often end up as scanned images inside the EHR, teams need strong integration between their fax solution and the core clinical systems. Softlinx outlines EHR integration patterns that tie cloud fax directly into registration, coding, and clinical workflows so that each faxed document lands in the right chart instead of a shared inbox.
From legacy fax machines to secure cloud fax and VoIP fax
Traditional fax devices rely on analog phone lines with no encryption. That weakness turns every outbound fax that carries PHI into a potential exposure point. Modern HIPAA rules for faxing medical records favor digital options that deliver better data security:
| Approach | Security profile | Role in a modern HIPAA compliance plan |
| Legacy fax machine on an analog line | No encryption, paper output, weak logging, and are often placed in public areas. | Suitable only as a stopgap, with strict physical safeguards, low PHI volume, and tight manual controls. |
| VoIP fax on the general phone system | Moves traffic to IP networks but can still lack full end-to-end encryption and audit trails. | Better than analog, but still often below the standard that a full HIPAA-compliant fax platform aims to provide. |
| Cloud fax integrated with EHR | Encryption in transit and at rest, strong authentication, role-based access, detailed audit logs, and direct links into the EHR and practice management system. | Often, the most practical route to meet HIPAA compliance requirements while staff to continue to send faxes through familiar workflows. |
Softlinx describes how fax through the internet, VoIP fax, and cloud fax differ in practice and how a cloud platform can still respect existing PSTN or SIP routes where needed. The company’s material on bulk fax APIs, electronic fax workflow automation, and API setup for healthcare applications shows how health systems can keep HIPAA rules for faxing medical records front and center while still modernizing infrastructure and reducing manual work.
Softlinx also explains in plain terms how to email a fax number inside a HIPAA-compliant framework, which can help physicians and care managers who live in their email client but still need fax for external partners.
Key takeaways on HIPAA fax rules for over-stretched compliance teams
| Key point | Why it matters |
| HIPAA permits faxing of PHI | HIPAA rules for faxing medical records do not forbid faxing; they require clear safeguards across Privacy, Security, and Breach Notification Rules. |
| Safeguards must match risk | OCR expects covered entities to apply reasonable administrative, physical, and technical safeguards; small clinics and large health systems both face scrutiny. |
| Patient rights still apply | Right of access, HIPAA patients’ rights, and release of information processes do not stop at the fax machine; they extend to every faxed document that contains PHI. |
| Cloud fax closes many gaps | A mature HIPAA-compliant fax service with EHR integration, audit logs, and encryption eases compliance pressure and helps prevent unauthorized access. |
| Policy plus technology wins | Written HIPAA fax rules, staff training, and modern cloud fax platforms together reduce the odds of a breach under HIPAA and simplify audits. |
Why these HIPAA fax rules deserve a place in your next risk review
HIPAA rules for faxing medical records touch almost every corner of a health system: front-desk registration, clinical teams, HIM, revenue cycle, and legal. Every fax that carries patient medical records reflects your stance on HIPAA compliance, HIPAA privacy, and HIPAA security in a single transmission.
If your current process still leans on stand-alone fax machines, shared trays, or ad-hoc email attachments, now is the time to map each workflow against HIPAA regulations and your own risk appetite.
A structured review that pairs written policy with secure technology cuts down on HIPAA violations, protects PHI in healthcare, and answers the recurring question “what information can be shared without violating HIPAA?” with clear, defensible rules.
Softlinx designs HIPAA-compliant cloud fax for hospitals, clinics, health systems, and enterprise partners that want stronger data security without extra friction for staff. If you want a practical path from legacy fax machines to a secure, auditable cloud fax platform that matches HIPAA rules for faxing medical records, explore the Softlinx healthcare cloud fax service and then request a quote for your environment:
Move from fax risk to fax control today with Softlinx. Visit the healthcare fax service and start a tailored discussion through Softlinx.
- November 27, 2025
Do I Need Special Equipment to Use a HIPAA Compliant Electronic Fax Service for Healthcare?
This article outlines the equipment requirements for implementing a HIPAA-compliant electronic fax service in healthcare settings. Healthcare providers often question whether transitioning from traditional fax machines requires significant infrastructure investments or specialized hardware.
The answer is straightforward: modern cloud-based fax solutions eliminate the need for dedicated fax machines, phone lines, or on-premise servers. Healthcare facilities can securely transmit patient information through existing devices, including computers, smartphones, tablets, and multifunction printers, while maintaining full compliance with the Health Insurance Portability and Accountability Act (HIPAA).
This guide examines the technical requirements, compliance standards, and practical implementation steps for electronic fax systems in medical practices, hospitals, and clinics.
Do I need special equipment to use a HIPAA compliant electronic fax service for healthcare?
The short answer is no. Healthcare organizations do not need special equipment to use a HIPAA compliant electronic fax service. Unlike traditional fax machines that require dedicated phone lines, fax servers, and physical hardware, modern electronic fax solutions operate through the internet on devices already present in most healthcare facilities.
A HIPAA compliant fax service works with standard computers, smartphones, tablets, and existing multifunction printers. The transition from legacy fax infrastructure to cloud-based fax systems eliminates hardware dependencies while strengthening security protocols for patient data transmission.
Healthcare providers can send and receive faxes through web portals, email clients, or direct integration with electronic health record systems. This approach removes the physical limitations of traditional fax machines and creates a more flexible document workflow that adapts to clinical operations.
What Equipment Healthcare Facilities Already Have
Most healthcare organizations possess all the necessary equipment to deploy electronic fax services immediately. The infrastructure requirements are minimal because cloud-based fax platforms leverage existing technology rather than demanding new investments.
| Device Type | Current Use in Healthcare | Electronic Fax Capability |
| Desktop Computers | Administrative tasks, EHR access, and billing | Web portal fax access, email-to-fax transmission |
| Laptops | Mobile clinical documentation, remote work | Full fax functionality from any location |
| Smartphones | Clinical communication, on-call duties | Mobile app access for urgent fax transmission |
| Tablets | Bedside documentation, patient rounds | Touch-optimized fax interfaces for quick access |
| Multifunction Printers | Document scanning, printing, and copying | Direct fax transmission from the device panel |
Standard office equipment becomes part of the fax infrastructure without modifications. A clinic administrator can transmit referral documents from their desktop computer through a web browser. Physicians can receive lab results as faxes directly in their email inbox.
Nurses can scan discharge paperwork on the department’s multifunction printer and route it to specialists through the printer’s interface.
The cloud fax approach transforms existing technology into secure transmission channels without requiring specialized fax hardware. Healthcare facilities avoid the capital expenditure associated with purchasing dedicated fax servers or maintaining analog phone lines for fax machines.
How does HIPAA view fax and electronic fax in healthcare?
HIPAA does not forbid fax. The HIPAA Privacy Rule allows a physician or healthcare organization to fax patient medical information to another provider for treatment, payment, or healthcare operations, as long as appropriate safeguards protect that information. The focus sits on the protection of patient data, not on a specific fax machine or device.
Key principles that shape any HIPAA compliant fax solution:
| Principle | What it means in practice |
| Device-neutral regulation | HIPAA does not declare one specific fax machine or fax app “approved”. It requires safeguards around any system that sends or receives patient information. |
| Safeguards over technology labels | Administrative, technical, and physical safeguards apply whether you use a traditional fax machine or a HIPAA compliant online fax service. |
| Vendor relationships | Covered entities must sign BAAs with any vendor that handles ePHI, including providers of HIPAA compliant fax services. |
| Documentation and oversight | Policies, procedures, and audit trails must show how your organization controls access to secure faxes and received faxes. |
In other words, Do I need special equipment to use a HIPAA compliant electronic fax service for healthcare? is less critical than the question of whether your faxing solution satisfies HIPAA requirements for encryption, access controls, audit logs, and BAAs.
A simple desktop fax machine with open paper trays can break HIPAA rules even though it looks familiar. A HIPAA compliant digital fax service that runs in the cloud, with audit trails and access controls, can meet HIPAA fax compliance without a single analog fax line on-site.
Softlinx describes these expectations in detail in its dedicated resource on HIPAA compliant fax requirements and how a HIPAA compliant fax service protects patient data inside healthcare workflows.
What your team actually needs on site
A HIPAA compliant fax service does not require specialized proprietary hardware in your facility. The table below sets out the usual components and whether they count as “special equipment”.
| Component | Typical reality in a healthcare setting | Special equipment required? | Why it matters for HIPAA compliant electronic fax |
| Workstations | Existing PCs or laptops for clinical and administrative staff | No | Staff send and receive electronic faxes through a secure web portal, EHR screen, or email client. |
| Network and internet | Existing secure LAN and internet connection | No extra hardware in most cases | The HIPAA compliant online fax platform runs in the cloud; your network only needs stable, secure access. |
| Physical fax machine | Legacy desktop unit in a corner office or nurses’ station | Not required | A modern HIPAA compliant digital fax service replaces the traditional fax machine; staff can still print when necessary, without relying on physical paper trays for PHI storage. |
| Fax server | Legacy on-prem fax server racks with fax boards and telephony connections | Not required with cloud fax | A HIPAA compliant cloud fax service removes the need for an in-house fax server and its telephony hardware. |
| Multi-function printers (MFPs) | Shared printers and scanners in departments | Optional | MFPs can still print received faxes or scan documents into workflows but no longer carry full responsibility for HIPAA fax compliance. |
| Telephony hardware | Fax boards, gateways, analog or PRI lines | Not required on your side with true cloud fax | The provider maintains secure fax telephony in the data center; your team connects through HTTPS and secure APIs. |
If you still run an internal fax system, Softlinx also explains legacy fax server setups and shows how to move away from on-prem fax hardware without disrupting clinical workflows.
Do I need special equipment to use a HIPAA compliant electronic fax service for healthcare in different care settings?
Healthcare still depends heavily on fax. Various industry sources have estimated that around seven out of ten healthcare organizations use fax in core information exchange, including referrals, prior authorizations, and diagnostic reporting.
That cuts across hospitals, outpatient clinics, and multi-specialty centers. Each type of organization asks the same core question in its own way: Do I need special equipment to use a HIPAA compliant electronic fax service for healthcare in my environment?
Hospitals
Large hospitals often maintain older fax server infrastructure with multiple phone lines and complex routing rules. A HIPAA compliant electronic fax service for healthcare replaces that hardware with secure cloud fax queues, role-based access for clinical and revenue cycle teams, and integration with EHR or document management systems.
For hospital teams, the “equipment” question turns into an integration question. Most hospitals already have an identity system, a security perimeter, and standard endpoints that can support a HIPAA compliant cloud fax service. No new proprietary boxes are usually required. Softlinx provides dedicated hospital cloud fax solutions that plug into existing clinical systems instead of forcing a new device layer.
Outpatient and primary care clinics
Smaller clinics often depend on one physical fax machine at the front desk, with inbound pages stacked in the open. That layout puts patient data at risk and can delay referrals or authorizations when staff step away.
A HIPAA compliant online fax service gives these clinics secure portal access from existing computers and tablets. The only new elements are user accounts in a secure fax application and basic staff training on password hygiene and folder use.
No new fax device is required. Softlinx tailors clinic cloud fax solutions so clinics can retire old fax machines while keeping familiar workflows for referrals, insurance forms, and lab results.
Medical centers and multi-site groups
Multi-specialty centers and large medical groups face volume as their main challenge. HIPAA compliant fax services that run in the cloud handle thousands of pages per day without on-site fax servers. Document traffic routes through encrypted channels to folders, MFPs, or EHR queues that staff already monitor.
Softlinx provides medical center cloud fax solutions for these environments, with encryption at rest, transport security, and full audit trails for every fax event.
Across all three settings, one conclusion stays consistent: Do I need special equipment to use a HIPAA compliant electronic fax service for healthcare has a stable answer. A proper HIPAA compliant fax service sits in the cloud, respects your existing hardware footprint, and focuses on security, workflow, and compliance rather than more devices.
Equipment vs responsibilities: who handles what in a HIPAA compliant electronic fax setup?
The greatest risk in healthcare fax rarely comes from the model number on the device. It comes from gaps in responsibilities and weak process control. HIPAA expects clear lines between the covered entity and the vendor. For a HIPAA compliant fax service, that split often looks like the table below.
| Area | What the cloud fax provider covers | What your healthcare organization covers |
| Core fax system | Secure fax telephony, virtual fax channels, delivery confirmation, and capacity management | Decision to retire or keep local fax machines during transition, and how those devices are used day to day |
| Security controls | Encryption at rest and in transit, firewall rules, intrusion detection, secure data center | Endpoint security on workstations, secure Wi-Fi, VPN policies, and patching on internal systems |
| Access controls | Role-based access within the fax application, secure login mechanisms, and session management | User account lifecycle, least-privilege policies, staff off-boarding, internal approvals for access changes |
| Audit trails | Detailed logs of sent, received, and deleted faxes, as well as view and download history | Review of logs, internal monitoring procedures, investigation, and documentation when something looks wrong |
| Compliance posture | HIPAA compliant cloud fax status, SOC audits, documented technical controls, and BAA terms | Risk analysis, HIPAA training, written policies for fax use, and internal compliance oversight |
| Integration | APIs, Epic and EHR integration kits, secure routing options to folders and applications | Choice of workflows, mapping of processes to integration paths, testing, and validation before go-live |
HIPAA guidance also expects covered entities to sign BAAs with third-party services that handle ePHI, including providers of HIPAA compliant fax services. Softlinx works as a HIPAA compliant fax service provider and offers BAAs that define each side’s duties.
For organizations that want to double-check the regulatory angle, Softlinx maintains a separate resource that responds directly to a frequent question: Is fax HIPAA compliant when you modernize your fax infrastructure and move to the cloud?
How Softlinx removes the need for special fax hardware
Softlinx focuses on HIPAA compliant cloud fax service for healthcare, finance, insurance, and other regulated sectors. The ReplixFax platform runs as a cloud-based faxing solution that removes the burden of local fax hardware and supports strict HIPAA fax compliance.
ReplixFax resides in a HIPAA-compliant, SOC-audited data center. Fax images and related metadata stay encrypted at rest, and all communication between your environment and the service uses secure transport protocols. These controls protect patient information without forcing you to install new fax boards or gateways inside your own network.
Access to this HIPAA compliant fax service runs through web applications, EHR integrations, and secure tools such as email-to-fax and print-to-fax drivers. Multi-factor authentication and role-based access govern who can send and receive faxes, who can view archived documents, and who can export data. This focus on access controls and audit trails addresses core HIPAA requirements and removes the need to lock down physical machines in every department.
For organizations that rely on Epic or other major EHR platforms, Softlinx offers specific integration paths so that staff can send and receive faxes directly inside the EHR. This approach lets healthcare teams treat fax as part of their normal clinical workflow rather than a separate, hardware-bound process.
Softlinx describes this approach in its cloud fax overview, where the emphasis sits on secure transmission over IP networks, reduced dependence on legacy phone lines, and a central HIPAA compliant fax solution instead of scattered devices.
For teams that want to see how this looks in practice, Softlinx also explains how to fax through the internet while keeping the security requirements of healthcare organizations intact and without adding new on-premise fax infrastructure.
So when a stakeholder asks, again, Do I need special equipment to use a hipaa compliant electronic fax service for healthcare with Softlinx?, the answer stays consistent: the heavy infrastructure runs inside Softlinx; your staff uses secured endpoints and applications that already exist in your environment.
Role of automation, workflow, and EHR integration
Once hardware moves off-site, the strongest value of a HIPAA compliant electronic fax service for healthcare appears in automation and integration rather than in the fax transport itself. Healthcare organizations still depend on fax for referrals, prior authorizations, lab results, claims, and discharge summaries; delays in these flows can affect patient care and revenue.
Surveys in the health IT space have reported that a high share of organizations, sometimes above 80% in specific samples, have seen fax-related delays influence patient care or financial outcomes.
A HIPAA compliant cloud fax service with automation routes inbound faxes to the right department, provider, or work queue. Fax numbers can tie to service lines, clinics, or individual clinicians, which reduces misrouted documents. Document classification and barcodes shorten manual indexing time, and integration with EHR or document management systems reduces repetitive data entry.
Softlinx examines these scenarios in detail in its guide on how to automate electronic fax workflow for business and healthcare operations, with real examples of routing rules, queue design, and alerting.
On the clinical side, Softlinx offers EHR integration paths so staff can send and receive secure faxes directly within the patient record. This model keeps clinicians in one system, lowers error rates, and makes HIPAA compliant faxing part of the documented care process rather than a disconnected step at a physical fax device. Softlinx’s dedicated HIPAA compliant fax service shows how hospitals, clinics, and medical practices use the platform to move lab results, orders, and authorizations securely, again without on-site fax servers.
Key takeaways
| Key point | Why it matters |
| HIPAA allows faxing with safeguards | Fax remains acceptable under the Privacy Rule as long as reasonable safeguards protect patient information before, during, and after transmission. |
| Focus on safeguards, not hardware | A traditional fax machine with open trays can break HIPAA rules; a HIPAA compliant online fax service with encryption and access controls can satisfy them without special equipment. |
| Cloud fax shifts infrastructure off-site | A HIPAA compliant cloud fax service runs telephony, storage, and encryption in the provider’s data center, which removes the need for local fax servers. |
| Existing endpoints are usually enough | Most hospitals, clinics, and medical centers already own the workstations and secure networks needed for HIPAA compliant faxing. No unique device is required. |
| Responsibilities must be defined | BAAs, policies, and audit reviews matter more than hardware purchases. Clear responsibilities between the provider and vendor support HIPAA compliance. |
| Integration improves patient care and efficiency | When fax flows inside EHR and workflow tools, staff spend less time chasing paper and more time on clinical work, while still meeting HIPAA compliance. |
Softlinx’s Healthcare Cloud Fax Services bring these pieces together for hospitals, clinics, diagnostic centers, and other providers that still rely on fax to move patient data. They focus on HIPAA-compliant fax solutions that use standard equipment on your side and advanced controls in the cloud.
Why your next fax decision matters more than new equipment
Healthcare still depends on fax for a large share of clinical and administrative communication, even with widespread EHR adoption and secure portals. As a result, your choice of fax strategy has a direct effect on HIPAA compliance, staff workload, and the reliability of information exchange between providers, payers, and partners. Effective Healthcare Fax Solutions can also help streamline care transitions by ensuring critical patient information reaches the appropriate providers quickly and securely.
Sticking with traditional fax hardware locks your organization into analog phone lines, on-site maintenance, and a security model built around doors and paper trays. A breach or misdirected document in that world can be difficult to trace and costly to fix.
A shift to a HIPAA compliant electronic fax service for healthcare changes the landscape. Fax becomes a controlled application service, with encryption, access controls, detailed audit trails, and documented BAAs that describe how patient information is protected.
Softlinx’s HIPAA compliant cloud fax service reduces dependence on physical fax machines and in-house fax servers, protects patient data with encryption and structured security controls, and connects to EHR and business applications so staff can send and receive secure faxes where they already work.
That path answers the question Do I need special equipment to use a hipaa compliant electronic fax service for healthcare? With a practical no, while also improving how your organization handles HIPAA fax compliance daily.
If your team wants to move away from fragile hardware, improve HIPAA fax compliance, and align fax workflows with modern healthcare IT, this is the right time to review your fax landscape. You can explore Softlinx’s broader secure cloud fax portfolio or speak with the team about a deployment that matches your environment and regulatory needs.
To discuss a HIPAA compliant electronic fax service for healthcare that fits your hospital, clinic, or medical group, start here: Request a secure healthcare fax assessment and quote from Softlinx.
- November 25, 2025
HIPAA Compliant Fax Requirements for Healthcare
Last year alone, healthcare data breaches exposed 276 million patient records. That’s roughly four out of every five Americans having their medical information compromised. Every day, another 758,000 records end up in the wrong hands. Healthcare organizations are scrambling to find secure ways to share patient information, and Healthcare Cloud Fax Solutions have become an important option for protecting sensitive data while maintaining efficient communication workflows.
While everyone talks about going digital, 70% of healthcare providers still rely on fax machines. Fax transmission has stuck around because it actually works well for secure document sharing when done correctly. The key phrase here is “when done correctly.”
Healthcare organizations that mess up fax security face average penalties of $3 million per violation. Beyond the financial hit, these breaches destroy patient trust that takes years to rebuild.
Breaking Down HIPAA Fax Rules
HIPAA doesn’t ban faxing. Actually, the regulations specifically allow fax transmission of Protected Health Information, but only when organizations follow certain rules. These rules are requirements that can make or break a compliance audit.
The administrative side covers who can send faxes and what information they’re allowed to transmit. Healthcare organizations need written policies that spell out these details. Staff training becomes crucial here because employees need to understand not just how to use the fax machine, but when they should and shouldn’t be using it.
Physical security sounds simple, but it trips up many organizations. Traditional fax machines need to sit in secure areas where random people can’t walk by and read incoming documents. This gets tricky in busy medical offices where faxes arrive at all hours. Too many organizations have fax machines sitting in break rooms or reception areas where anyone can see confidential patient information.
Old School Fax vs. Modern Solutions
Traditional fax machines use regular phone lines, which gives them an advantage under HIPAA’s “conduit exception.” Healthcare providers don’t need special agreements with phone companies because the phone system just carries the signal. However, this doesn’t mean traditional faxing is automatically secure, which is why many organizations are adopting Healthcare Fax Solutions that provide stronger security controls and compliance support.
The biggest problem with old fax machines is human error. Staff members dial wrong numbers all the time, sending patient records to complete strangers. Understanding how to prevent HIPAA violations when faxing starts with recognizing that most breaches aren’t technical failures, but simple human mistakes during transmission. By reducing manual dialing, verifying recipients, and using systems with built-in safeguards, healthcare organizations can significantly lower their risk. Even when organizations program frequently used numbers into the machine, people still make mistakes. Mix-ups happen when numbers change or when similar numbers get confused.
Modern hipaa compliant fax services solve many of these problems. Cloud-based systems encrypt everything automatically and keep detailed logs of all activity. Many integrate directly with Electronic Health Records and other healthcare software. This means less manual work and fewer chances for mistakes.
The practical benefits go beyond security. Internet fax lets healthcare workers send and receive documents from anywhere with an internet connection. Emergencies become more manageable when doctors can access patient information from home or other locations. Plus, fax through the internet eliminates the hassle of maintaining phone lines and physical machines.
What Makes Fax Systems Compliant
Building a truly compliant fax system requires several pieces working together. Encryption protects patient information as it travels between locations and while it sits stored on servers.
User authentication keeps unauthorized people out of the system. Multi-factor authentication adds extra protection by requiring users to prove their identity in multiple ways before accessing sensitive features. Larger healthcare organizations especially need this because so many people need fax access for their jobs.
Access controls limit what different users can do based on their roles. A medical assistant might be able to send certain types of documents but not others. A physician might have broader access. These controls help ensure people only see information they need for their specific job duties.
Comprehensive logging captures every fax activity – who sent what, when it happened, where it went, and whether it succeeded or failed. These logs become critical evidence during compliance audits or security investigations. Organizations that can’t produce detailed logs often face bigger penalties when problems occur.
Cover sheets provide an extra layer of protection. HIPAA-compliant cover sheets warn recipients that they’re looking at confidential medical information and explain what to do if they received it by mistake. While encrypted online systems make cover sheets less critical, they’re still good practice.
Getting Implementation Right
Successful fax security goes beyond just buying the right technology. Organizations need solid procedures for verifying recipient information before sending anything. This might mean calling to confirm fax numbers or maintaining centralized contact lists that get updated regularly.
Document handling procedures matter from start to finish. Staff need clear guidelines on how to prepare documents, which transmission method to use, and what to do when something goes wrong. Training programs should emphasize double-checking recipient information before hitting send.
Transmission monitoring helps catch problems quickly. Modern systems usually provide immediate status updates showing whether documents arrived successfully. When transmissions fail, staff should know exactly what steps to take for retransmission or alternative delivery.
Storage policies govern what happens to faxed documents after transmission. Digital copies need secure storage with proper access controls. Incoming faxes require the same security treatment as any other patient information.
Choosing the Right Fax Service
Healthcare organizations face many options when selecting fax solutions. Business Associate Agreements top the list of must-haves for any third-party service. These legal contracts establish exactly what the vendor must do to protect patient information.
Encryption standards determine how well patient information stays protected. Look for services offering 256-bit encryption or better, covering both data transmission and storage. Some services add features like encrypted email delivery for received faxes.
Integration capabilities can dramatically improve workflow efficiency. The best hipaa fax solutions work seamlessly with existing Electronic Health Records, practice management software, and other healthcare applications. Good integration reduces manual data entry and maintains security throughout the entire process.
Compliance certifications provide extra assurance about vendor security practices, especially when evaluating what compliance certifications a cloud fax provider should have. SOC 2 Type II, HITRUST, and similar healthcare security certifications show that vendors undergo regular security audits and maintain appropriate protections.
Scalability and reliability ensure the service can grow with the organization while maintaining consistent performance. Consider transmission volume limits, uptime guarantees, and support availability. Healthcare organizations often need fax access outside normal business hours, making 24/7 support valuable.
Common Implementation Problems
Staff resistance to new technology can slow adoption and create security gaps. Comprehensive training programs help by emphasizing both security benefits and workflow improvements. Hands-on training sessions work better than just handing out manuals.
Cost concerns influence many technology decisions, but organizations must weigh implementation costs against potential HIPAA violation penalties. With average fines exceeding $3 million, proper security measures represent good financial planning. Consider total costs including implementation, training, maintenance, and potential audit support.
Legacy system integration challenges organizations with existing healthcare IT infrastructure. Success requires vendors offering flexible integration and adequate technical support during transitions. Phased implementation can minimize disruption while maintaining security standards.
Multi-location coordination becomes complex for healthcare systems operating across multiple sites. Centralized management platforms provide consistent security policies while accommodating local workflow needs. Cloud-based solutions often work well for multi-location scenarios.
| Feature | Traditional Fax | Cloud Fax | Encrypted Email |
| Built-in Encryption | No | Yes | Yes |
| Automatic Logging | No | Yes | Sometimes |
| Advanced Access Controls | Basic | Yes | Yes |
| Multi-Location Support | Limited | Excellent | Good |
| Software Integration | None | Extensive | Good |
| Requires BAA | No | Yes | Yes |
| Setup Difficulty | Easy | Medium | Medium |
| Ongoing Maintenance | High | Low | Medium |
Preparing for Tomorrow’s Compliance Requirements
Regulatory updates will likely bring additional security requirements. The Department of Health and Human Services has proposed major HIPAA Security Rule changes that could impact fax transmission requirements. Organizations should monitor these developments and prepare for compliance changes.
New security technologies offer promising improvements. Artificial intelligence can support secure transmission through automated recipient verification, content scanning, and intelligent routing. These features may become standard in future HIPAA-compliant fax solutions.
Healthcare organizations that address communication security proactively position themselves for success while protecting patient trust and avoiding violations. The data shows breaches keep increasing, making strong security measures essential rather than optional.
Healthcare providers looking to improve their communication security should consider professional consultation services. Softlinx specializes in helping healthcare organizations implement comprehensive, compliant communication solutions that protect patient privacy while improving efficiency.
Get a quote and secure cloud fax for your healthcare business.
For More:
- September 15, 2025
Choosing Secure Fax Services for the Medical Industry
Faxing still has a place within many healthcare organizations, providing an effective way to send and receive protected health information (PHI). However, there’s recently been a shift to cloud-based secure fax services, allowing for improved usability and security of that shared information.
Healthcare providers must choose a fax provider carefully, guaranteeing the security of PHI at all times while also ensuring providers and staff have access to and can operate the system easily. Healthcare Cloud Fax Solutions allow users to easily transmit data in a digital format through a secure internet connection using high-level encryption, real-time data transfers, and other capabilities.
Here are some things people in the medical industry need to know about how to choose a secure fax service.
How Online Fax Services Work
“The cloud” is any software or service provided over the internet; a cloud fax service replaces physical fax machine or on-premises fax server with internet-based, outsourced service options. A dedicated phone line or fax machine isn’t necessary with cloud-based faxing, nor does it need an on-premises fax server that requires system maintenance and/or upgrades with internal IT staff involvement.
Instead, Healthcare Fax Solutions enable organizations to take digital files and send them through a secure platform using a special email address that includes the recipient’s fax number or an easy-to-use web interface. The service provider converts uploaded documents into the proper format, encrypts them, and sends them to the recipient. When receiving, the provider converts the document into a readable format and delivers the fax securely.
A cloud-fax service offers 100% compliance with HIPAA and other regulations.
How To Choose an Online Fax Service
Follow these steps when choosing an online fax service:
1. Assess your needs.
First, you’ll need to know the realistic volume of faxes that will need to be sent and received. Additionally, prepare a list of fax document workflow and processing requirements so you know ahead of time what the fax service will need to provide.
2. Reach out to vendors.
Start by researching top online fax service providers and reading about their offerings, as well as investigating past and current customer reviews. Reach out to the top vendors for more information.
Ask for representative to explain all included features and how they handle customer service needs, and ensure the product meets your needs. At this time, you can evaluate both their product and customer service.
3. Understand cost and fees.
Hidden fees and unexpected costs can make budgeting difficult, so ask about overall pricing and any other charges you could face throughout the contract.
4. Request a demo.
Most providers offer a free product demonstration or trial period, so take advantage of this. Test the service before you finalize the purchase to see how it works and better understand if it will work for your needs. For example, is it user friendly? Does it provide necessary features and capabilities for managing your faxing and document control needs? Does it integrate with your back-office document workflows? What is the capacity and performance?
You should also ask about additional tools that can integrate with your current technology or other features the service offers (such as custom cover sheets, delivery to network folder, broadcast faxing, preset delivery times, or folder-based faxing).
5. Make sure the secure fax service is HIPAA-compliant.
Ask vendor about whether their product is HIPAA compliant and what features are in place such as:
- Control over access to customer PHI.
- Data encryption during transmission and while at rest in the cloud.
- Cybersecurity insurance coverage.
- Finding and protecting against anticipated cybersecurity threats and information theft.
Ultimately, the service should take steps to guarantee all PHI availability, integrity, and confidentiality.
Additionally, ask the vendor if they can share their Annual SOC 2 Type II audit report and Application Penetration Test report with you. Also ensure they would sign Business Associate Agreement (BAA).
Benefits A HIPAA-Complaint Fax Service Should Have
Cloud faxing, or online faxing, has a variety of benefits including greater flexibility, security, and efficiency. For example, cloud-based fax services:
- Provide secure transmission. Criminals cannot hack into a fax to steal data, and even if it is somehow hacked or intercepted, the third party can’t read it without conversion by an authorized user. Faxes deployed with data encryption can make faxes more reliable and secure, which is essential when sending and receiving PHI.
- Send a secure fax immediately. Data traveling uninterrupted from a fax sender to a recipient is less susceptible to hacking. Cloud faxing sends faxes directly to an individual, and the user who wants access must provide correct credentials. You’ll then receive confirmation that the intended recipient gets the fax.
- Keep costs down. There’s no need to purchase, operate, or maintain a separate fax machine or on-premises fax server, or have a dedicated phone line. You’ll save internal IT staff time because there isn’t an on-premises fax server or network systems. Cloud faxing also reduces paper waste.
- Are easy to use. Managing incoming and outgoing faxes is as simple as having access to a computer or mobile device and internet connection – no other equipment is required. Immediate service activation doesn’t require a long lead time, and user-friendly online tools allow you to send and receive faxes anywhere.
Plus, Softlinx also offers a customer web portal with comprehensive fax administration features, making managing fax users and secure fax activities easy.
Enhance productivity. Using a cloud fax service streamlines healthcare fax workflows and significantly simplifies faxing tasks. This helps staff work more efficiently, eliminating challenges like managing junk faxes or dealing with paperwork, refilling paper or ink, or other maintenance.
Trust Softlinx with Secure HIPAA-Compliant Faxing
Our HIPPA-complaint cloud faxing services and other solutions can help you achieve smarter document-handling protocols while protecting PHI. Request a demo today or call (800) 899-7724.
- February 15, 2023
What Measures Are Necessary for Faxes to Meet HIPAA Regulations?
Privacy laws like the Health Insurance Portability and Accountability Act (HIPAA) play a critical role in the healthcare industry, governing how organizations handle sensitive information. If you transmit patient health information via fax, this standard applies to you.
This guide will discuss how privacy laws affect faxing and how to ensure HIPAA compliance with faxes.
What Is HIPAA?
The Health Insurance Portability and Accountability Act is a federal law passed in 1996 to protect sensitive patient health information. Based on this law, national standards were established to prevent health information from being disclosed without patient knowledge or consent.
The U.S. Department of Health and Human Services enforced the requirements of HIPAA by issuing the HIPAA Privacy Rule. This set of standards addresses how organizations use and transmit health information to protect the privacy of those who seek care. These guidelines aim to protect patients’ health information by setting use limitations while still allowing for high-quality healthcare delivery.
How Does HIPAA Impact Faxing?
While most individuals don’t associate HIPAA and faxing with one another, these terms share a crucial connection. If you work in healthcare, you likely transfer sensitive patient information using faxes. HIPAA laws require that you protect this data during utilization and disclosure, which includes faxing.
The majority of healthcare offices use faxes to transmit patient information. If any of these facilities send sensitive information to the wrong recipient, they can incur serious HIPAA penalties for noncompliance. That’s why healthcare organizations must use fax solutions optimized for HIPAA compliance to minimize the risk of accidental disclosure.
HIPAA-compliant faxing solutions have security features like data encryption, page-by-page confirmation and real-time data transfer. These safeguards prevent patient information from being compromised or misdirected.
The Difference Between Meeting HIPAA Regulations With Online Fax Versus Traditional On-Premises Fax
Healthcare providers that use traditional on-premises fax solutions experience difficulty meeting HIPAA compliance standards due to the many security challenges posed by these outdated technologies. With advanced online fax solutions, organizations can send a HIPAA compliant fax securely and seamlessly.
Fax Machine Access
Traditional fax machines can print incoming patient health information at any time, leaving physical copies of this information temporarily unattended on the printer. This lack of access control can pose serious patient privacy and security risks by leaving information exposed.
Through online cloud faxing, incoming faxes are transferred to the intended recipient using their unique fax number, preventing the information from being misdirected. The patient information is also encrypted, so it can only be read by authorized individuals.
Fax Cover Sheets
All faxes containing patient health information must have a protective cover sheet as required by HIPAA. This cover sheet indicates that the document includes confidential health information and is not to be transferred to another party without express patient consent, in the absence of which it must be destroyed.
Online faxes allow you to customize your cover sheets to include all required disclosures and enforce them by department, user, or across the entire organization. These capabilities make Healthcare Fax Services an effective way to maintain compliance while streamlining document workflows.
Fax Transmission Records
When transmitting paper faxes, senders must create and retain confirmation copies containing transmission and transaction log summaries, along with the date, time and the recipient’s fax number. Online fax technologies take detailed records of all your fax transmissions and receipts, making report generation effortless.
Received Fax Security
Traditional on-premises faxing requires that received faxes be securely stored immediately upon removal from a physical fax device. Cloud-based faxing solutions send received faxes directly to the intended receiver’s email. Once the fax has been sent, all data and images within the fax are wiped from the faxing platform to prevent access by third parties.
How to Ensure HIPAA Compliance With Faxes From Softlinx
At Softlinx, we offer Healthcare Cloud Fax Services to help healthcare facilities protect their patients’ sensitive health information. We’ve spent over 20 years providing our customers with innovative enterprise information technology (IT) solutions to help them optimize their document workflow processes and maximize profits.
We offer a HIPAA compliant electronic fax service called ReplixFax for the healthcare industry. This system is designed to protect confidential patient information while maintaining business continuity through safeguards such as:
- Advanced data encryption.
- Safe data transmission over secure IP networks.
- Secure centralized storage.
- Intrusion detection and prevention.
- Multifactor authentication.
ReplixFax maintains detailed logs of all faxes, retrievals, deletions and inquiries to facilitate audits. Due to our secure network, our data center is fully compliant with the American Institute of Certified Public Accountants (AICPA), HIPAA and Payment Card Industry Data Security Standard (PCI DSS) standards.
Send HIPAA Compliant Faxes With Solutions From Softlinx
You can bridge the gap between HIPAA and faxing with HIPAA compliant fax services from Softlinx. When you outsource your faxing to cloud services with us, we’ll help you leverage greater cost savings, productivity and compliance.
Schedule a free live demo to explore our solutions today!
- October 11, 2022
The Importance of HIPAA-Compliant Fax Cover Sheets
Implementing safeguards for medical privacy laws per the Health Insurance Portability and Accountability Act of 1996 (HIPAA) is crucial for all healthcare organizations, whether protected information is communicated over the phone or via email. As long as the patient provides their consent, healthcare providers can safely send and receive protected health information (PHI) via encrypted emails or Healthcare Cloud Fax Services. Cover sheets are only one piece of the picture, so it helps to know the full HIPAA rules for faxing medical records before sending any chart. However, obtaining the patient’s consent is not enough — the fax must be HIPAA compliant per the federal law restricting the release of medical information.
Learn more about the importance of medical HIPAA compliant fax cover sheets and other technical safeguarding measures healthcare organizations can use to protect ePHI.
What Are PHI and ePHI?
Protected health information is any health information with a patient’s personal identifiers, such as a name, date of birth or social security number. Any PHI that is electronically transmitted, whether by email or fax, is known as ePHI.
Why Do Faxes Need a Cover Sheet?
Because a cover sheet is the first thing the recipient will see when they open the fax, it is a physical barrier of protection. A medical HIPAA compliant fax cover sheet is a technical safeguard to deter accidental viewing and disclosure of protected information.
What Should a HIPAA Fax Cover Sheet Contain?
There are a few fields all HIPAA compliant fax cover sheets should include to keep the sender and the unauthorized recipient safe from an unintentional data breach. If you opt to download a free cover sheet template online, be sure to check for the following fields:
Patient/HIPAA Information
- The patient’s name and reference number
- The date and time you sent the fax
- A HIPAA cover sheet disclaimer
Sender Information
- Name of the individual sender
- Name of the covered entity or organization
- The sender’s fax number and phone number
Recipient Information
- Name of the individual recipient
- Name of the recipient’s organization
- The recipient’s fax number and phone number
Why HIPAA Fax Compliance Still Matters in the Digital Age
Despite the rise of electronic health record systems and secure email platforms, faxing remains a widely used method of communication in the healthcare industry—especially among small practices, pharmacies, and insurance providers. Because of this, maintaining HIPAA compliance for fax transmissions is just as important today as it was two decades ago. A single misstep, like omitting a HIPAA fax disclaimer or sending to an incorrect number, can result in data breaches, regulatory fines, and loss of patient trust. That’s why implementing reliable, cloud-based fax solutions with built-in compliance features and standardized fax cover sheets is a proactive way to protect sensitive health information while ensuring operational efficiency.
Best Practices for Creating a HIPAA-Compliant Fax Cover Sheet
To minimize the risk of data breaches and ensure your organization remains HIPAA compliant, it’s essential to follow best practices when designing and using medical fax cover sheets. A well-structured HIPAA-compliant fax cover sheet can enhance security, streamline workflows, and reinforce your organization’s commitment to patient privacy.
Here are key best practices for creating effective HIPAA fax cover sheets:
-
Use a standard template approved by your compliance officer or legal department.
-
Avoid including sensitive PHI on the cover sheet itself—only reference the patient’s name or unique identifier when necessary.
-
Display a clear and bold HIPAA disclaimer at the top or bottom of the page.
-
Include sender and recipient contact details to aid in immediate correction if the fax is misdirected.
-
Mark the fax as “Confidential” or “Private” prominently to alert recipients.
-
Include a fax transmission log or request a delivery receipt to ensure secure and documented delivery.
-
Update cover sheet templates periodically to comply with the latest federal regulations or institutional policies.
Following these best practices ensures that your HIPAA fax transmissions remain compliant, especially in fast-paced healthcare environments where secure information sharing is critical.
What Is an Example of a HIPAA Fax Disclaimer?
Your fax cover sheet will also require a HIPAA disclaimer. A HIPAA disclaimer serves to:
- Notify the recipient the fax contains classified patient health information.
- Safeguard against unauthorized viewing if the recipient is unfamiliar with HIPAA regulations.
- Protect the covered entity from liability should the information be viewed, copied or distributed.
A HIPAA disclaimer is reasonably straightforward by nature. First, it should state that HIPAA protects the fax’s enclosed information. Second, it should specify that if the recipient is not the intended individual or entity, they must contact and inform the sender of receipt and arrange the fax’s return or destruction.
Like cover sheet templates, you can find HIPAA fax disclaimer examples online. Here’s ours:
IMPORTANT: This fax contains confidential information, some or all of which is protected health information defined by the federal Health Insurance Portability & Accountability Act (HIPAA) Privacy Rule. This fax is exclusively intended for the entity or individual to whom it is addressed because it contains proprietary, privileged, protected and/or exempt information that is exempt from disclosure by federal law.
If you are not the addressed recipient (or an employee or agent responsible for delivery of this fax transmission to the intended individual or entity), you are hereby notified that disclosure, dissemination, copying, or distribution of the information enclosed is prohibited and you may be subject to legal restriction or sanction. Please notify the sender via telephone to arrange the return or destruction of the information enclosed and all copies.
Why Should Organizations Use a HIPAA Fax Cover Sheet?
It may surprise healthcare providers to learn HIPAA regulations don’t definitively state you need to include a cover sheet when you send protected information via fax. However, a HIPAA fax cover sheet is the simplest way to deter unauthorized disclosure of sensitive information if the fax arrives in the wrong hands. A fax cover sheet’s overall purpose is threefold:
- It provides the sender’s contact information so the unintended recipient can inform the sender.
- It tells the recipient to whom the fax was sent to encourage them not to look at the contents if not permitted to do so.
- It protects the covered entity from liability should the fax be illegally viewed, copied or distributed.
What Other Measures Can You Take to Ensure Privacy?
Outside of using a HIPAA fax cover sheet and disclaimer, there are other practices you can carry out to ensure the safe delivery of protected information.
- Verify the fax number: Occasionally, fax numbers change or are entered incorrectly during sending. Before you send a fax, call the intended organization to verbally confirm with a representative that the fax number you have on file is up to date.
- Notify your recipients: Call the organization to notify them when you send protected information. You can do this when you call to confirm the fax number, but even if you’re confident the fax number is correct, it is best to inform the intended recipient the information is coming their way — in case the fax fails or delivers to the wrong number.
- Print a delivery confirmation: Once the fax is successfully delivered, print the delivery confirmation for physical documentation. You can also review the printed delivery confirmation to confirm the fax number one last time. Occasionally, you may not notice an error — especially if it is a single digit — until you see the number in print.
Frequently Asked Questions (FAQ)
Do I legally need a HIPAA fax cover sheet?
While HIPAA doesn’t explicitly mandate a cover sheet, it does require appropriate safeguards to protect PHI. A HIPAA-compliant fax cover sheet is a recommended technical safeguard that helps prevent unauthorized access to sensitive health data.
What makes a fax cover sheet HIPAA compliant?
A HIPAA-compliant cover sheet must include sender and recipient information, the date and time of transmission, a confidentiality statement or disclaimer, and a clear indication that the fax contains protected health information (PHI).
Can I use a standard fax cover sheet template?
Yes, but it must be reviewed and customized to include all HIPAA-required elements. Many free templates online are not fully compliant unless they include proper HIPAA disclaimers and omit sensitive PHI.
Is email-to-fax HIPAA compliant?
It can be—if the service provider uses proper encryption and the fax includes a HIPAA-compliant cover sheet. Services like ReplixFax are designed with these standards in mind.
What should I do if a fax is sent to the wrong number?
Contact the unintended recipient immediately, request that they destroy the fax, and document the incident. You may also need to report the breach depending on its severity and your internal HIPAA compliance policy.
Send Secure, HIPAA Compliant Faxes With ReplixFax
Many healthcare organizations opt for cloud-based faxing with Healthcare Fax Services as a convenient method for creating HIPAA-compliant faxes. ReplixFax streamlines HIPAA compliance for healthcare providers and administrators with secured storage networks, Advanced Encryption Standard (AES) encryption, and other built-in safeguards. Our solutions are audit-friendly, enhance communication between EHRs, and facilitate multidevice access for combined convenience and compliance.
In short, we ensure your ePHI healthcare faxes deliver seamlessly and compliantly. We’ve designed our cloud-based fax services with busy, patient-centered healthcare organizations in mind. Our ReplixFax cloud fax service is easy to use on the go thanks to its intuitive interface, saving healthcare providers and administrators valuable time and energy. Using our email-to-fax interface, sending a fax is as simple as attaching a file to an email, addressing it to the recipient’s fax number and hitting send.
Contact us today to migrate your faxing to the cloud with our HIPAA-compliant cloud fax service for healthcare organizations.
- April 14, 2022
What Are the Benefits of HIPAA-Compliant Cloud Fax Services?
There are many advantages to incorporating Healthcare Cloud Fax Services into your healthcare operations. Aside from the daily ease of more streamlined business processes, these HIPAA-compliant, cloud-based faxing systems help bring peace of mind that your fax communications and activities align with the healthcare industry’s strict governance requirements.
Healthcare administrators and practitioners have enough on their plates without the headache of a complex fax system. When you must continually spend time checking and double checking fax information, shoring up its security, updating internal policies and training on the latest software with the newest compliance features, you are directly inhibiting one of the most perfunctory aspects of healthcare administration.
You can make your faxing and online document deliveries streamlined and secure through Healthcare Fax Solutions while taking advantage of a host of additional benefits, such as these four.
1. Enhanced Compliance & Patient Confidentiality
Adhering to HIPAA’s stringent industry rules is a leading concern for healthcare institutions and their partners. However, ensuring your practices are HIPAA compliant takes time, money and continual resources, both on the human and technical side.
With a secure, cloud-based fax delivery system, you directly streamline nearly all aspects of medical document communications that are still critically used today. This not only means quicker and more efficient services within your office, but the risk of in-compliance is off your shoulders — unlike when you have manual faxing or on-site fax servers.
The following items bolster this enhanced compliance:
- Business Associate Agreements (BAA): BAAs serve as chains of trust for all levels of healthcare providers, vendors and subcontractors. According to HIPAA, anyone with access or potential access to PHI must sign and adhere to these contracts. ReplixFax has built-in user logs, notifications and authorized access controls that complement BAAs and PHI-handling best practices, ultimately meeting HIPAA compliance.
- HIPAA-Audited Data Center: Your faxing service platform is managed and hosted at an SSAE-16 audited data center. This means you have a top-of-the-line facility, computer systems and data-management team regularly scrutinized under HIPAA’s evolving requirements, year to year.
- Compliance Management Partners: The cloud-based nature of the system means you have a 24/7 resource to support your critical fax data. This partner is just as responsible for its management and must be as well-versed in HIPAA regulations as you are, reinforcing your holistic risk-management practices.
2. Heightened Data Security
Some of HIPAA’s strongest regulations center on the safeguards and protection of PHI. Considering healthcare is one of the most-hacked industries today, its vast swaths of stored medical history and sensitive data mean healthcare service organizations cannot rest on their laurels. Institutions must continually be vigilant, monitoring their networks, setting up cyber-security defenses and partnering with vendors to help mitigate today’s and tomorrow’s risks.
It’s no easy task, but a comprehensive HIPAA-compliant fax service system can help you accomplish this with the following features:
- Designated Sign-In: Anyone sending a fax or working with system data must first sign into their individual, password-protected account.
- Fax Encryption: While at rest within the cloud-storage system, all faxes, files and their inputted protected health information (PHI) sit encrypted through a AES 256-bit encryption method, one of the most advanced in the industry.
- Fax Data Recovery: The loss of patient data will not only interrupt a healthcare organization’s or vendor’s operations — it puts real people at risk. Your reputation sits at stake without a routine data-backup system in place to recover PHI and faxes in the event of an emergency or cyber threat.
- Automatic Notifications: You can set up notifications to alert both senders and receivers when a fax has been initiated. This means sharper, real-time communication and better fax management, with fewer instances of sensitive data sitting in a queue.
- Authorized Access: You can set up your cloud-based fax API with authorized-only access, which gives system log-ins only to a select few individuals. This directly reduces the chance of unauthorized data access, viewing, transferring and overall in-compliant handling.
3. Streamlined Auditing
Another aspect of HIPAA compliance concerns the thorough and secure documentation of information, transactions and procedures. HIPAA-compliant faxing is no different, and agencies that do not have proper audit trails in place risk severe fines and repercussions if they are found to be incompliant.
The sheer amount of faxes and fax-related communications procured in the healthcare industry necessitates a complete, streamlined auditing system that logs and accounts for every piece of correspondence. With a cloud-based fax API system, you get the following:
- Complete Data Log: The fax API system maintains a record of all file activities, including additions, deletions, retrievals, transfers and data search queries. This is square one in a straightforward audit trail protocol for yourself or your medical clients.
- User Activity Log: The system registers all user activity, which you can then search and catalog using current administrative tools or other integrated web services APIs.
- Fax Trails: The system logs every incoming and outgoing fax, meaning you have one central repository for fax audit trails. Any audit request or compliance check has a straightforward accountability system in place.
- Annual SOC2 Reports: This is a complete report on the data center hosting your PHI, detailing its service environment, practices, updates and procedures, so you can rest assured your data management remains HIPAA-compliant.
- HIPAA-Compliant Fax Deletion: The system allows for industry-standard electronic file deletion, simplifying another compliance headache for many healthcare institutions or hosting vendors.
4. Simpler Software Integration
You can harmonize your’s or your client’s current computer programs and applications through tailored Web Service APIs. This software integration minimizes disruptions to your business operations, reduces employee training and allows operations to remain active. Plus, with more streamlined software suites, you can take care of tasks like converting HIPAA-compliant fax to emails or HIPAA-compliant link sharing in a few simple clicks.
Some other features of this integration include:
- Safe Fax Delivery: Send faxes using safer, security-enhanced delivery channels, either via email-over-TLS or Web-over-secure links.The sheer amount of faxes and fax-related communications procured in the healthcare industry necessitates a complete, streamlined auditing system that logs and accounts for every piece of correspondence. With a cloud-based fax API system, you get the following
- Safe Communications Portal: All communications enacted through the Web Service API come as encrypted links using premier Secure Sockets Layering (SSL) protocol.
- Fax Data Corrections: Reduce the likelihood of human error and improper data inputs. Replix Healthcare Fax can pull fax numbers and other simple data from your existing fax directories, including popular systems like LDAP, Microsoft Active Directory and IBM Domino Address Books.
- Complementary Administrative Tools: You can incorporate other administrative and fax-management tasks into Replix Healthcare Fax through Web Service API.
What Can Your Healthcare Organization Accomplish With HIPAA-Compliant Fax Services and Support?
It’s not just about saving time and money. A complete, HIPAA-compliant fax solution for your medical or healthcare organization alleviates the oversight and energy it takes to remain in compliance, which is square one for those in the industry.
These cloud-based faxing programs also put people first — from your office administrators to your patients themselves. As concerns over data privacy and usage only grow more pressing, you can rest assured your organization is taking every possible measure to secure medical information and meet the public’s heightened demands.
A Replix® HIPAA-compliant fax solution from Softlinx is your partner in doing so. Schedule a free live software demo today at (800) 899-7724, email our support specialists, request a quote online or fill out our contact form.
- November 12, 2020
Why You Should Use a Secure Fax
Updated for 2025
Is online fax secure? That is one of the most frequently asked questions among people who have yet to find a secure fax service. If you’re still unsure about online faxing, this guide will answer everything you need to know about using an online fax service.
What Is Secure Fax?
A secure fax is a digital document that is encrypted for security over fax servers. A secure fax cannot be intercepted, stolen or accessed by unauthorized third parties. On a secure fax, the numbers of both the sender and the recipient are hidden from view to protect both identities. Secure faxes are protected with strong encryption and impossible to read until they arrive in the hands of recipients.
Many of today’s businesses are employing cloud fax service companies to safely fax sensitive document with utmost confidentiality.
How to Send a Secure Fax
When you need to send documents in as safe a format as possible, your best option is to use a secure cloud fax service. Online secure fax services keep documents safe from interception while in transit between senders and receivers as well as while at rest in the cloud. Compared to traditional faxing methods, digital faxing offers the following benefits:
1. Encrypted Systems
Correspondence via digital fax is done over an encrypted system that is far safer than Ethernet, WiFi or phone lines. This makes digital fax a far safer and more secure medium of communication than either traditional fax or email, which both occur over lines that could easily be hacked or intercepted by a third party.
Traditional faxing is done over phone lines, rendering such documents vulnerable in situations where a line has been bugged by an information thief. If, for example, your company is infiltrated by someone who intends to steal information and pass it onto a third party, that individual could possibly bug your phone lines and make it possible for the competing entity to receive incoming and outgoing fax messages.
When matters of safety are taken into consideration, email correspondence is also trumped by the digital faxing option. If someone sends a document to your email inbox, that document is passed through Ethernet cords that are similar in nature to phone lines. Moreover, emails are vulnerable to hackers and data breaches. In the medium of digital fax correspondence, each exchange is protected by layers of security that are impossible to penetrate with phone bugs and email phishing tactics.
2. Flexibility
With digital faxes, you can choose to receive the documents on an email server or a fax machine. Furthermore digital fax servers can also deliver your faxes into secure network folders or directly into your business applications. As such, the faxing medium offers a range of choices that email itself simply lacks. If the documents in question are of a sensitive nature, you would definitely want to restrict the exchanges to faxing devices. This, of course, would be the option to take if the documents involve signatures, social security numbers or credit card information.
If the documents are benign and contain no sensitive data, you may opt to receive them as emails or faxes. For faxes that merely concern promotions or party invites, you might wish to receive them as email correspondence.
3. Legally Binding Documents
When it comes to legally binding documents, email remains an unacceptable medium. Given the aforementioned problems associated with email, there are too many risks involved with emailing legal documents. For starters, there is no way for a party that requests a signature to verify the authenticity of a signature when it arrives in the form of an email message.
Legal documents are one of the main reasons why fax, both traditional and digital, has remained popular in the face of email and online correspondence. Fax has always been an accepted medium for legally binding documents because the issuing party can verify that the signature is indeed authentic.
If a document is signed in paper form, the authenticity of the signature is obvious due to the handwriting of the signature itself, whether the document is signed in ink and returned via snail mail or returned via fax. If a document is signed electronically on a digital fax form, the signature is verifiable since the document itself can only be processed on the computing device of the intended recipient of the original blank document. Therefore, faxed documents are generally accepted as legally binding, barring those submitted to government agencies.
4. Hack-Proof Documents
Cyber thieves can hack into email servers and leak the private data of targeted parties. Instances like these have collapsed businesses, ruined careers, destroyed reputations and put people at risk. Despite the efforts of email service providers, who have worked with anti-malware developers to block the intrusions of data thieves, hacking remains a problem for many users. For each new fortification in cybersecurity, hackers up the ante and find new ways to bypass security code.
With faxes, there is no equivalent to the hacking issue because cybercriminals cannot hack into a fax to steal data. You never have to worry about unauthorized foreign parties cracking the code on a fax to access your private info. Simply put, faxes rely on a different type of technology that cannot be intercepted by third parties. Even if an unauthorized party intercepts a fax communication, the thief would not actually be able to steal any data from incoming or outgoing faxes because the data would need to be converted for readability and only the sender or receiver could authorize that task.
5. No Spam
One of the biggest differences between the mediums of fax and email is the flow of spam, a problem solely confined to the email medium. Since the rise of email back in the mid-1990s, the word
“spam” has been common parlance among even the most entry-level Internet users. You will inevitably receive spam the moment you give an email address to anyone outside your closest personal confidants.
Thankfully, today’s most broadly used email servers are equipped with functions that filter spam into separate folders, allowing users to avoid the majority of unwanted messages. Still, the very presence of spam as an ongoing problem — one that everyone with an email address has had to deal with at some time or another — points to the very real security issues of email as a medium. The fact that you can end up on spam lists simply for listing your email address on social media, even in the most limited capacity, points to the real and clear danger of exchanging sensitive data through email correspondence.
In the medium of fax correspondence, there is no equivalent to spam. Even if your fax number falls into the hands of a bulk-list hard seller, it is illegal to send junk faxes because doing so uses up the toner and paper of parties at the receiving end. Therefore, digital and traditional fax correspondence is free of the plague of spam or anything of a similar nature.
6. No Blocking
With email, problems can arise with the blocking features that are generally designed to protect users. The blocking features are intended to filter out spam and messages with dangerous attachments. However, various other messages can get scooped into blocking filters due to characteristics that are not always easy to pinpoint. For example, you might send an important business email to a potential client or partner, only for that message to end up in the recipient’s spam folder. While the individual might have enacted steep, indiscriminate filter functions, the problem could easily be down to the wording of the email header.
When important emails end up in other people’s spam filters despite your own best intentions, you could end up missing out on various opportunities. This is one of the other main reasons why faxes are better than email when it comes to business correspondence.
With faxes, there is no such thing as a blocking function because faxing has no equivalent to spam. In the majority of cases, faxes are anticipated and warmly received on the other end. Even when a fax is not expected in advance, it will generally be received well due to the pre-established relations between the two parties. After all, you are unlikely to receive outright junk faxes because the practice is illegal. If someone sends you a fax, it would probably be for something that you already anticipate signing and returning or responding to in some other positive way.
7. Instant Confirmation
One of the biggest advantages of fax correspondence is that you can verify whether the message has been received at the other end. With traditional fax, you are notified the moment the fax is either auto-printed or placed in a queue at the receiving end.
When you send a document via fax, you get the instant assurance that your message or document was received on the other end, regardless of whether the recipient is there to view it at the time in question. In that regard, you can feel a sense of accomplishment when you send a fax because you will have completed your end of the exchange, regardless of whether the other party responds.
Is Faxing Documents Secure?
When you use an online fax service, the following practices can help your organization keep security tight:
- Make sure that your fax service provider uses strong encryption to keep your documents protected and secure while they are in transmission or at rest in the cloud. Choosing secure Healthcare Cloud Fax Services can help ensure sensitive healthcare communications remain protected and compliant.
- If you forward a fax that contains portions of information deemed confidential by the original sender, make sure to crop the info in question before you forward the fax to the third party.
- Before sending a fax, contact the intended recipient to verify they will be available to receive the fax. This step is especially crucial if the fax communication involves a deadline or anything that requires prompt action at the other end.
- If a fax concerns matters of high confidentiality, refrain from sharing said fax with organizations that engage in weak confidentiality practices.
- Enact a retention policy within your organization and among partnered entities to ensure that faxed communications via email, both sent and received, are not retained beyond their intended expiration dates.
- Fax services typically retain logs of outgoing and incoming communications. It is, therefore, crucial to read and understand the privacy protections and retention policies of a service provider.
Cloud-based fax services are safe and efficient as long as the medium is used with the utmost responsibility.
Is Using Email Safer Than Sending Faxes?
Email has been around since the 1980s and remains popular for many reasons. When compared to the fax, email servers provide quality in the following areas:
1. Password Protection
For basic privacy, email is a safe medium for basic correspondence in most situations. Email servers are protected by login and password prompts. These prompts will not grant access if the wrong info is entered into the fields. If you enter the wrong username or password twice in a row, the email server will usually block your IP address. You will then need to verify your identify and reset your information, typically through a secondary email address or possibly via phone verification.
With strict login prompts and security protocols, email is generally a secure medium for the majority of daily communications that do not involve legal documents or sensitive business data. That said, the vulnerable aspects of email have rendered the medium inappropriate on all but the most encrypted servers for communications between elected officials and government personnel.
2. Firewalls
Most of today’s email services protect users with firewall functions. These filter out suspect emails and block the activation of attachments that could be dangerous, such as .exe files. Therefore, today’s email platforms are far safer than the early programs that most people used back in the late ‘90s and the early ‘00s when it was not uncommon for extension files to execute and infect hard drives. These days, such problems are rare on most email servers. In fact, few of today’s younger users have ever had a computer crash or OS infection originate from a corrupt email.
Email is generally viewed unfavorably as a means of communications among serious organizations. This is because of its checkered past. To a large extent, these attitudes are justified. Email servers are not foolproof. Some of the biggest horror stories from yesteryear could still occur in isolated scenarios. As such, businesses, government agencies and other high-security organizations refrain from using email servers for all but the most casual and inconsequential correspondence.
The advent of mobile text messaging, which is commonly practiced among work colleagues, has largely replaced email.
3. Privacy
In many ways, email is one of the most private mediums of communication between people who are not in the same room. While you can talk to someone on a phone, other people nearby might overhear your side of the conversation. You could exchange messages on an online forum or on social media, but all such posts could easily be seen by other people who use those platforms, even if you use high-privacy settings. With email, the only person who sees the message is the user with access to the inbox in question.
In this regard, email correspondence has the advantage over traditional faxing. A fax could potentially be seen by anyone with access to the machine at the receiving end. If you run a busy office space where dozens of people from various departments pass by the fax receptor each hour, no communication sent via conventional fax could really be considered private. This is one reason why modern Healthcare Fax Solutions focus on secure digital delivery methods that help protect sensitive information while maintaining compliance requirements.
Granted, if you are the only person with access to a particular fax, the privacy risks would be less substantial. However, that gets beyond the intended purpose of faxing, which is generally for two parties to instantly exchange secure and often legally binding documents across great distances.
Basically, faxing has the advantage over email in terms of security. On the other hand, email has the upper hand in terms of privacy. If you need to send sensitive data or a signed document to someone in a different department, building, city, state or country, use fax. If you want to reveal something touchy about your personal life to a close friend afar, use email.
Why You Should Use Fax Instead of Email
In all the debates about fax vs. email security, most people agree that faxing is the better option for documents of a sensitive or highly classified nature. Email lacks the safety of fax for the following reasons:
1. Email Attachments
Emails can come with dangerous attachments. These attachments can infect your computer and possibly spread to other machines linked to the same network. If you work in an office and receive an email purported to be of interest to your business, it could possibly have a virus attached. This virus will execute on your hard drive the moment you open the message.
The scary thing about email attachments is how they are sometimes difficult to spot. Even if you do realize that an email has some type of malware attached, it could be impossible to stop the infection by the time it comes to your attention.
These days, people are largely desensitized to the threat of harmful email attachments. This is because it is often assumed that Windows will detect such problems in advance and suppress them. Therefore, employees are often naive about the potential threat of email viruses. Moreover, certain types of malware are designed to run in the background of a machine and steal info. This can happen unbeknownst to the user of an infected machine.
Faxed documents, by contrast, never pose such a threat because there is no way to attach malware to a fax.
2. Email Hacking
Another major risk of email correspondence is the possibility of third-party hacking. If you and a colleague are discussing confidential business information via email, those messages could be accessed by an unauthorized party and leaked into the wrong hands. It could either be a rival within your company or a competitor looking to harm your business in some way.
When email accounts are hacked, the intrusion is virtually impossible to detect. Most victims of email hacking only learn of the situation the hard way, such as when information is leaked to the Internet. Depending on the sensitivity of the information in question, an email leak could cause a company to unravel.
With secure digital faxing, there is no risk of third-party hacking because the information in transit would merely consist of unreadable code that can only be translated on the machine of the recipient.
3. Phishing
Another major risk of email is the possibility of phishing. Phishing is generally defined by messages from an ostensibly friendly source. These emails contain fetching links. The moment you click one of these links, popup prompts appear on your screen that ask for basic personal info in a misleading but seemingly benign manner. Even though many email users are wise to such gambits in this day and age, many people still fall for this trap. Your company might have a naive employee who takes the bait and unwittingly puts the whole network at risk.
In some cases, programs will open that take over your computer. These programs execute inescapable prompt boxes the moment you open the message. Phishing is basically designed to access vital company data. This may include contact lists, credit card numbers and the passwords of program account holders. In a worst-case scenario, a phishing incident could lead to a data breach of epic proportions. This could cause you to lose customers by the thousands.
Thankfully, phishing is not possible with secure digital faxing.
Secure Fax Service From Softlinx
Secure fax is becoming the most accepted way for B2B communication. If you constantly engage in fax communications to and from your customers and contacts, you should definitely employ the services of a cloud fax service. Contact Softlinx for a demo or get a quote.
- July 17, 2019