A cloud fax provider should support HIPAA compliance with a signed BAA, third-party security audits such as SOC 2, strong encryption, role-based access control, audit trails, and industry-specific safeguards such as PCI DSS when payment data may pass through fax workflows. HITRUST, ISO 27001, FedRAMP, NIST alignment, and data residency controls may also matter depending on your industry, risk profile, and regulatory duties. Fax did not disappear from regulated business. It changed shape.
Hospitals still send referrals. Insurance teams still move claims. Banks still exchange signed records. Government offices still depend on secure document transfer. A manufacturing team may need to send supplier paperwork, while a college may need to protect student or HR files. In each case, fax remains part of daily work because the process is accepted, documented, and familiar to outside partners.
The problem starts when fax moves from a machine in the corner to a cloud-based fax platform. At that point, the buying decision is no longer just about whether the tool can send a document. Compliance, access, audit history, data protection, and vendor responsibility all come into the room.
That is why many IT and compliance teams now ask the same question before they choose a provider: what compliance certifications should a cloud fax provider have? The answer depends on the kind of data your organization sends, where that data lives, and who may access it after the fax is sent or received.
For healthcare organizations, the conversation usually starts with HIPAA, protected health information (PHI), and a signed business associate agreement (BAA). Implementing secure Healthcare Fax Solutions helps organizations maintain compliant document exchange while supporting privacy and operational requirements. For finance teams, PCI DSS and audit controls may be more urgent. For government buyers, NIST alignment, FedRAMP expectations, and data residency may matter. For enterprise IT, SOC 2 is often the document procurement wants to review before a contract moves forward.
This guide explains the certifications, agreements, security controls, and buyer questions that matter when choosing a cloud fax service. It also shows how a HIPAA-compliant cloud fax platform such as Softlinx ReplixFax fits into the wider compliance conversation.
Softlinx is especially relevant for U.S. organizations that need secure cloud fax workflows across healthcare, insurance, finance, government, manufacturing, and higher education.
What Compliance Certifications Should a Cloud Fax Provider Have?
A cloud fax provider should have the compliance support that matches the documents your organization sends, receives, stores, and routes.
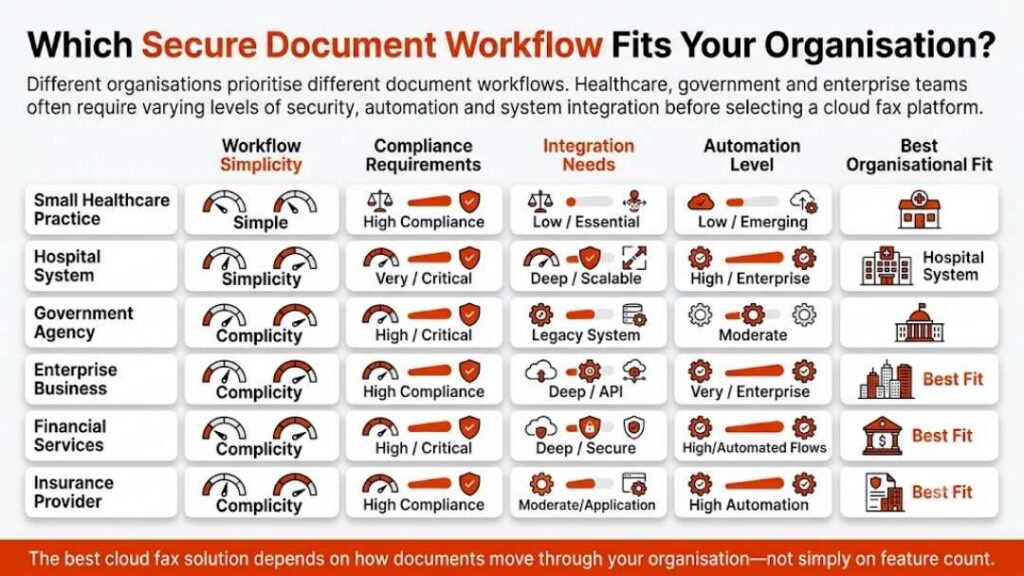
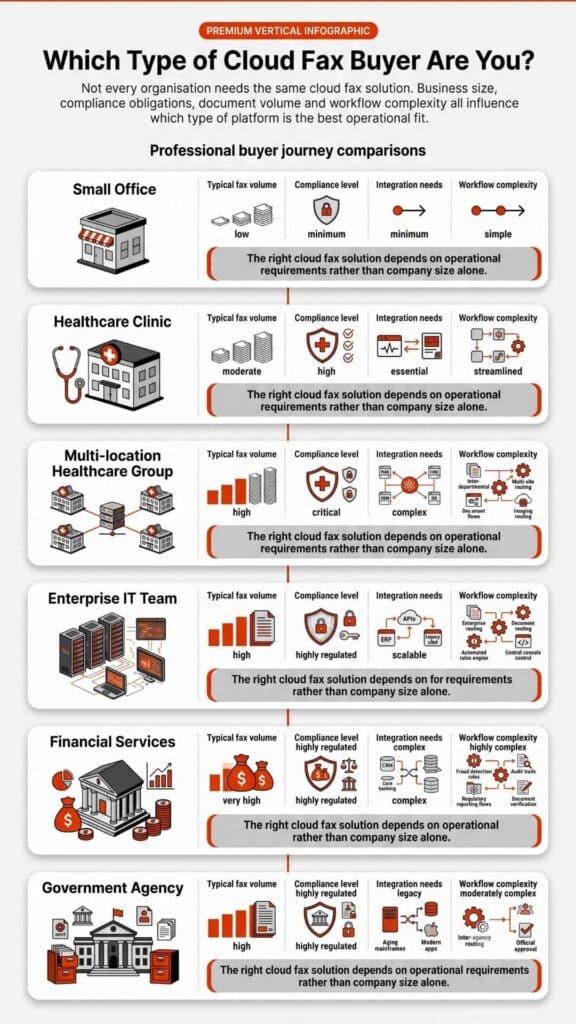
There is no single certificate that makes every cloud faxing solution safe for every industry. A clinic that sends patient records has different obligations from a finance department that may handle payment forms. A city agency may have different needs from an insurance claims team or a high-volume medical billing company.
Still, several standards appear again and again during cloud fax reviews. HIPAA support with a signed BAA is essential for healthcare. SOC 2 Type II gives buyers a stronger view of tested security controls. PCI DSS matters when payment account data may enter the fax workflow. HITRUST can add deeper healthcare assurance. ISO 27001 can support broader information security governance. NIST alignment or FedRAMP may matter in public-sector settings.
| Compliance item | What it helps prove | Who should pay close attention |
| HIPAA support plus BAA | The provider accepts defined responsibilities for PHI and ePHI | Healthcare providers, payers, labs, billing firms, pharmacies, medical practices |
| SOC 2 Type II | Security and operational controls were examined over a period of time | Enterprise IT, compliance teams, procurement, regulated businesses |
| PCI DSS | Controls exist for environments that store, process, or transmit payment account data | Financial services, billing departments, insurance teams, payment-related workflows |
| HITRUST | A healthcare-focused risk and control framework has been assessed | Hospitals, health systems, payers, healthcare SaaS vendors |
| ISO 27001 | The provider follows a formal information security management system | Global companies, enterprise buyers, risk-led organizations |
| FedRAMP or NIST alignment | Security expectations fit public-sector or federal cloud use cases | Agencies, contractors, government-adjacent organizations |
| Data residency controls | Customer data can be handled according to location and storage requirements | Multistate, international, or highly regulated organizations |
The right answer depends on the use case. A small clinic may focus on HIPAA, a BAA, encryption, access control, and audit trails. A health system may ask for those same safeguards plus SOC 2 reports, penetration test summaries, EHR integration details, and support for department-level fax numbers. A bank may ask how secure faxes that include account information are stored and reviewed. A public agency may ask where customer data sits and who can access it.
A strong cloud fax buying process looks beyond compliance logos. It asks for documentation, technical controls, workflow safeguards, and clear answers.
HIPAA Compliance Is a Requirement, Not a Marketing Badge
Healthcare buyers often search for phrases such as efax HIPAA, HIPAA online fax, cloud fax HIPAA, or best HIPAA-compliant fax. The wording changes, but the concern is usually the same: can this provider handle medical information without adding avoidable risk?
A better question is more specific. Will the provider sign a business associate agreement BAA? Does the platform protect protected health information PHI in transit and at rest? Can administrators decide who sees each fax number, user queue, department inbox, document, and report? Are audit trails available when compliance staff needs to see who did what?
The U.S. Department of Health and Human Services states that a HIPAA-covered entity or business associate may use a cloud service to store or process ePHI “provided the covered entity or business associate enters into a HIPAA-compliant business associate contract or agreement (BAA)” with the cloud service provider.
That line matters because HIPAA is not a badge a vendor can casually place on a page. If a cloud provider creates, receives, maintains, or transmits ePHI for a covered entity or business associate, the relationship needs proper legal and security structure. The BAA should define how ePHI may be used, how it must be safeguarded, what happens if there is a breach, and which responsibilities belong to the provider.
So, is fax HIPAA compliant? It can be, but only when the full process is controlled. A traditional fax machine in a hallway may leave patient pages exposed. A poorly managed email-to-fax process may send PHI to the wrong inbox. A HIPAA-compliant cloud fax service with encryption, MFA, role-based access control, secure routing, user activity reports, and a signed BAA gives teams more control over the workflow.
For healthcare teams, HIPAA-compliant cloud fax for healthcare should be judged by real use cases: referrals, prescriptions, authorizations, lab reports, billing files, imaging records, and inbound triage. Healthcare Cloud Fax Solutions need to protect documents while also fitting the way staff already work
SOC 2 Type II: The Audit Buyers Should Ask About
SOC 2 is one of the most useful trust signals for enterprise cloud fax buyers. It does not replace HIPAA, and it does not make a provider compliant with every regulation. What it can do is give buyers a better view of the provider’s control environment.
The AICPA describes SOC services as assurance reports that help users assess and address risks tied to outsourced services. The Trust Services Criteria cover security, availability, processing integrity, confidentiality, and privacy. For cloud fax, those areas matter because the platform may store documents, route messages, manage users, and process sensitive customer data.
A SOC 2 Type I report reviews whether controls are suitably designed at a point in time. A SOC 2 Type II report is more useful for most buyers because it reviews whether controls operated over a period of time. That distinction matters. Compliance teams do not only want to know whether a control exists on paper. They want to know whether it works during normal business activity.
If a provider claims secure faxes are encrypted, a SOC 2 review may support the larger story around access control, change management, monitoring, vendor oversight, incident response, and system availability. It does not remove the customer’s own compliance duties, but it makes vendor due diligence more grounded.
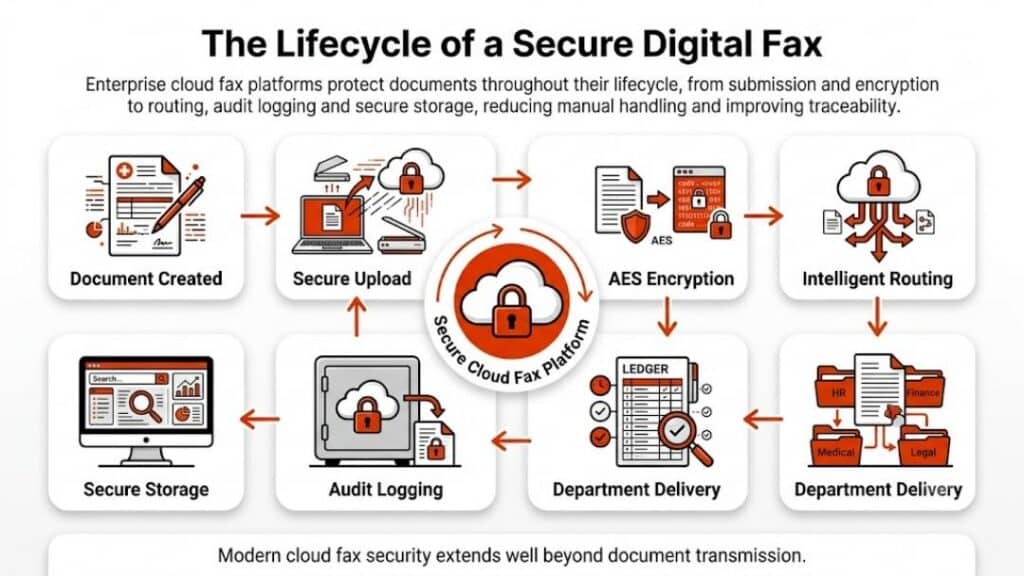
Organizations that send high-volume fax traffic should pay close attention here. A busy claims office, diagnostic center, hospital, or finance team needs more than a login screen. It needs dependable queues, traceable delivery, secure storage, delivery status, controlled user access, and administrative oversight.
Softlinx positions ReplixFax for regulated organizations that need secure document workflows, multiple fax methods, and central control. Buyers who want to compare technical requirements can review enterprise cloud fax controls before they choose a provider.
HITRUST: Stronger Assurance for Healthcare Fax Workflows
HITRUST often appears in healthcare vendor reviews because it gives organizations a structured way to assess security and privacy controls. It is not always mandatory. Many healthcare organizations work with vendors that do not hold HITRUST certification. Still, hospitals, health systems, payers, and healthcare SaaS companies may value it during procurement.
The reason is straightforward. Healthcare data moves through many hands. One patient record may touch a physician office, imaging center, lab, pharmacy, payer, billing company, and care coordinator. Fax often sits between those groups because they may not share the same EHR, portal, or document system.
If a cloud fax provider has HITRUST, that may support a stronger risk story. If it does not, the buyer should look for other evidence. SOC 2 reports, documented security controls, penetration tests, vulnerability tests, MFA, access reviews, encryption, incident response procedures, secure storage, audit trails, and a signed BAA all deserve attention.
In healthcare, the core issue is not the certificate name alone. The real question is whether the provider can help keep protected health information PHI under control from the moment a user clicks attach the document to the moment the fax reaches the right recipient, gets logged, and stays available only to approved users.
That is why HIPAA compliance fax should be treated as a workflow standard, not a slogan. A provider may advertise HIPAA faxing, but buyers still need to ask how inbound faxes are routed, how failed transmissions are handled, how fax numbers are assigned, how access changes when staff leaves, and how audit history can be reviewed.
PCI DSS: Important When Fax Workflows Touch Payment Data
Not every fax contains payment information. Still, real business workflows are rarely neat. Payment authorization forms, billing records, insurance paperwork, loan documents, and account updates may be sent between teams via fax. When payment account data enters that workflow, PCI DSS becomes relevant.
The PCI Security Standards Council says its standards are developed and maintained to protect payment data throughout the payment lifecycle. PCI DSS provides baseline technical and operational requirements designed to protect payment account data.
That does not mean every cloud fax customer has the same PCI scope. It does mean buyers should ask better questions. Can payment-related faxes be separated from general traffic? Who can open them? How long are they retained? Are documents encrypted? Is there an audit trail? Can access be limited by department, role, or fax number? How does the vendor protect customer data in storage and during transmission?
These questions matter for banks, lenders, billing departments, insurance operations, credit unions, brokerages, and any organization that uses fax to move sensitive financial documents. A provider that supports secure transmission, administrative controls, encryption, and audit logs can help teams see who touched what and when.
Softlinx states that ReplixFax supports HIPAA- and PCI-DSS-compliant cloud fax workflows. For buyers in finance, the broader review should connect those controls to internal policies, customer data handling, and account-document workflows. A useful next step is to review secure faxing for financial services.
ISO 27001, NIST, FedRAMP, and Data Residency: When Extra Assurance Matters
Some organizations need more than HIPAA, SOC 2, or PCI DSS. This is especially true when cloud fax is part of a larger vendor risk program.
ISO 27001 can be useful when buyers want evidence of a formal information security management system. It is not specific to fax, but it can support vendor trust when documents, metadata, user profiles, logs, and customer data move through a cloud platform.
NIST alignment may matter when organizations follow federal or public-sector security practices. Government agencies, contractors, and government-adjacent organizations often ask vendors to map controls to NIST frameworks or related requirements.
FedRAMP is narrower. It applies to cloud products used by U.S. federal agencies and sets a formal authorization process. Not every cloud fax provider needs FedRAMP, and not every buyer should demand it. But when a federal agency plans to use a cloud fax platform, FedRAMP status or a clear discussion of government cloud requirements may become part of procurement.
Data residency also deserves attention. A cloud fax provider may store inbound faxes, outbound fax records, metadata, user accounts, logs, and attachments. If an organization has contractual, regulatory, or internal policy limits on where data can live, the provider should be able to explain hosting locations, backups, retention settings, subcontractors, and access controls.
These requirements are not decorative. They tell buyers whether the provider can fit into a serious risk program without creating extra work for IT, legal, and compliance teams.

Compliance Controls Matter as Much as Certificates
Certificates and audit reports matter. Daily controls matter just as much. A HIPAA-compliant web fax platform should make secure behavior easier for staff. If the system is clumsy, people find shortcuts. Someone prints a fax that should stay digital. Someone forwards a file to the wrong inbox. Someone uses a shared login because the right access was never created. Strong cloud fax design reduces those weak spots by giving teams practical controls.
| Control | Why it matters in cloud fax |
| AES 256-bit encryption | Helps protect stored fax documents and sensitive files |
| TLS or secure transmission | Helps protect data while it moves between systems |
| Role-based access control | Limits who can view, send, download, route, or manage secure faxes |
| Multi-factor authentication | Adds protection when passwords are stolen or reused |
| Audit trails | Shows who sent, received, viewed, routed, or changed fax activity |
| User activity reports | Helps compliance teams review behavior and access patterns |
| Retention controls | Reduces unmanaged document storage and supports policy-led cleanup |
| Fax number management | Keeps department, user, and location numbers under administrative control |
| Secure workflow routing | Helps direct inbound faxes to the right queue, team, or application |
| Administrative oversight | Gives IT a clearer view of users, permissions, queues, and delivery status |
These controls also answer common search questions such as are faxes HIPAA compliant and is a fax HIPAA compliant. Fax can be part of a compliant process, but only when the process includes the right safeguards.
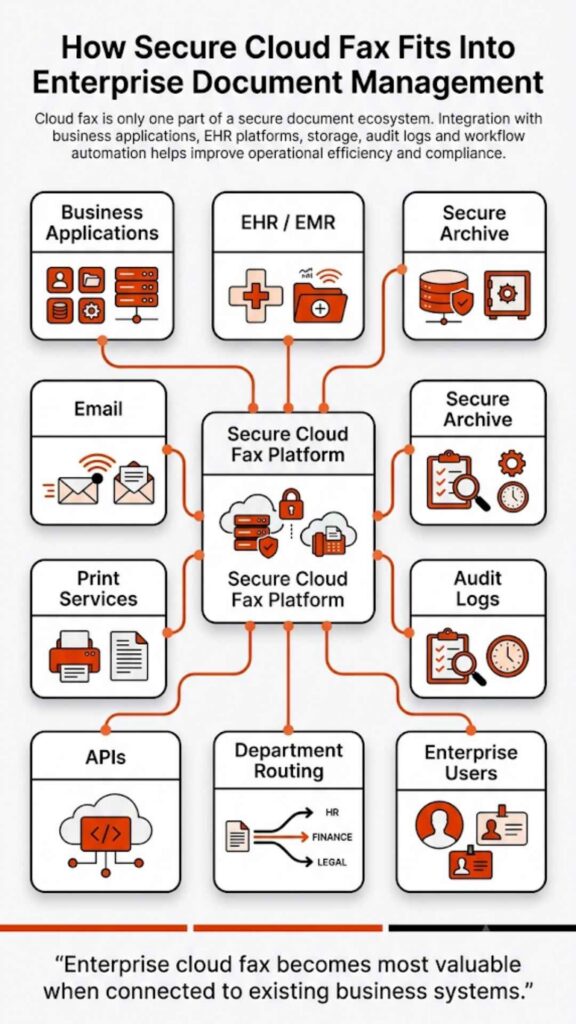
A cloud fax service that supports MFA, audit logs, and role-based access control gives administrators more visibility than a shared machine. A system that routes incoming records to a secure queue can reduce the chance of PHI sitting on paper. A platform that connects fax traffic to business applications can also reduce manual sorting and missed documents.
For teams that need more structure, fax workflow automation can help route documents to the right team without relying on one person to watch a machine, refresh an inbox, or sort pages by hand.
Cloud Fax vs Traditional Fax: Which Is Easier to Govern?
Traditional fax has one clear advantage: people know it. That familiarity explains why fax has stayed in healthcare, insurance, finance, government, and education for so long. But familiar does not always mean easy to govern.
A fax machine may sit near a front desk, nurses’ station, records room, or shared office. Pages may print before the right person arrives. Confirmation sheets may be filed manually. Staff may need to scan paper back into another system. If the wrong number is dialed, the mistake may not be caught right away.
A secure cloud faxing solution works differently. Faxes can move through user accounts, department queues, web portal access, email-to-fax rules, print-to-fax workflows, APIs, or application integrations. The provider still needs strong controls, but administrators have more ways to manage users, logs, routing, retention, and access.
| Compliance area | Traditional fax machines | HIPAA-compliant cloud fax |
| Access control | Depends heavily on physical location and office habits | Uses login, MFA, user permissions, and role-based access control |
| Audit trail | Often limited to machine logs or manual records | Provides digital fax logs, delivery records, and user activity history |
| PHI exposure risk | Paper can sit in an output tray or shared room | Documents can route to secure inboxes or controlled queues |
| High volume work | Busy lines, paper handling, and manual sorting can slow teams down | Scalable fax queues and workflow rules can support heavier traffic |
| Remote access | Hard to manage without workarounds | Approved users can work through secure portal or configured email-to-fax |
| Retention | Often tied to paper files, scans, or local storage | Digital retention settings can support policy-led document control |
| Number management | Lines and devices may be spread across locations | Fax numbers can be managed centrally by department or user |
Cloud fax is not compliant by default. A weak provider can still create risk. But a well-governed cloud fax platform gives compliance teams more visibility than traditional fax equipment.
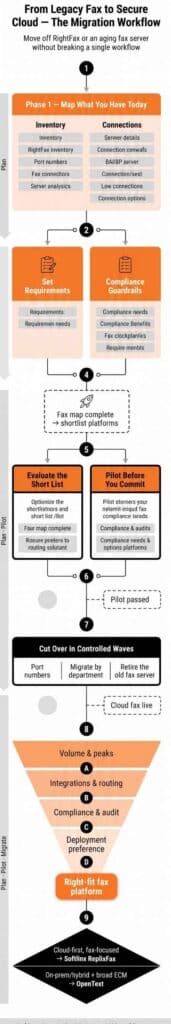
For organizations still tied to hardware, it may help to review how teams can switch from a fax machine to cloud fax without disrupting daily document exchange.
What Healthcare Teams Should Ask Before Choosing a Cloud Fax Provider
Healthcare buyers do not need vague reassurance. They need answers that stand up in procurement, compliance review, and real clinical work.
The first question is whether the provider will sign a business associate agreement BAA. Without that, a vendor that handles PHI is usually not a fit for HIPAA-related fax workflows. The second question is whether the provider can explain how data is protected in transit and at rest. Encryption should not be hidden behind sales language.
The next questions should move into workflow. Can staff send HIPAA online fax messages without exposing PHI through ordinary email? Can inbound records route by fax number, department, or document type? Can administrators review audit trails? Can access be removed quickly when a staff member changes roles? Can users attach the document from approved systems without downloading files to unsafe local folders?
Healthcare teams should also ask about EHR and application workflows. A hospital, imaging center, laboratory, or outpatient clinic may not want fax to live in a separate silo. If faxes support referrals, discharge paperwork, prescriptions, orders, results, or prior authorizations, the cloud faxing solution should fit existing clinical and administrative processes.
For organizations that rely on Epic workflows, Epic fax integration can help connect fax activity to patient record processes. For IT teams that build fax into internal systems, a cloud fax API may matter just as much as the web portal. For large outbound workloads, high-volume production fax workflows may also deserve review.
The best HIPAA compliant fax provider is not the one with the loudest claim. It is the one that can explain how compliance requirements, security design, support, and workflow fit together.
What Compliance Certifications Should a Cloud Fax Provider Have for Each Industry?
The phrase what compliance certifications should a cloud fax provider have means different things in different industries. A dental office, bank, claims administrator, city office, factory, and university may all use fax, but they do not answer to the same risk framework.
| Industry | Compliance priorities | What buyers should verify |
| Healthcare | HIPAA, BAA, SOC 2, encryption, PHI controls, audit trails | The provider signs a BAA, protects PHI, supports secure routing, and offers healthcare-ready controls |
| Insurance | SOC 2, HIPAA where health data is present, secure claims routing, access logs | Claims documents can be routed, reviewed, and traced without broad access |
| Financial services | SOC 2, PCI DSS, privacy safeguards, account data controls | Payment and account documents are protected through encryption, access control, and audit history |
| Government | NIST alignment, FedRAMP where applicable, auditability, data residency | The provider can discuss public-sector security expectations and data handling |
| Manufacturing | SOC 2, secure supplier document exchange, role-based access | Business documents can move between departments, suppliers, and partners with controlled access |
| Higher education | FERPA-aware records handling, SOC 2, access control, HR privacy | Student, employee, and administrative records are not treated like ordinary office paperwork |
Insurance buyers may need secure claims routing, records control, and department-level queues. A good next step is to review insurance claims fax workflows and compare them with internal claim intake procedures.
Public-sector buyers may need more formal documentation. For those teams, government cloud fax workflows should be reviewed through the lens of auditability, user control, and data handling.
Manufacturing teams often care about secure operational documents, supplier communication, production records, and order-related paperwork. In that setting, cloud fax for manufacturing should support document control across sites and teams.
For colleges and universities, fax may still touch student records, HR files, financial aid documents, medical forms, or administrative requests. A secure platform for higher education fax workflows should give departments more control than shared machines and manual filing.
Red Flags That a Cloud Fax Provider May Not Be Ready for Compliance
A cloud fax provider does not need every certification in the market. But it should be able to answer direct compliance questions without hiding behind vague language.
One red flag is a refusal to sign a BAA for healthcare use cases. Another is a broad claim such as “HIPAA secure” with no explanation of encryption, user controls, audit logs, or vendor responsibility. If a provider cannot explain how it protects PHI, who can access customer data, or what happens after a failed fax, the review should slow down.
Lack of MFA is another concern. So is the absence of role-based access control. A shared login may seem convenient, but it weakens accountability. If several staff members use the same account, audit trails cannot clearly show who viewed, sent, downloaded, or routed a document.
Vague retention rules also create risk. A provider should be able to explain how long faxes are stored, whether customers can set retention policies, and what happens when documents are deleted. For regulated teams, unmanaged storage is not a small detail.
Another warning sign is poor support for high-volume fax needs. Some platforms work well for occasional sending but become harder to manage when hundreds or thousands of pages move through queues. Healthcare billing firms, insurers, diagnostic centers, and enterprise offices should ask about throughput, routing, delivery status, number management, reporting, and operational support.
Buyers should also be cautious when compliance sounds like a sales phrase rather than a documented process. Real compliance work is specific. It covers agreements, controls, reports, testing, logs, access, data protection, and incident handling.
Where Softlinx Fits in the Compliance Conversation
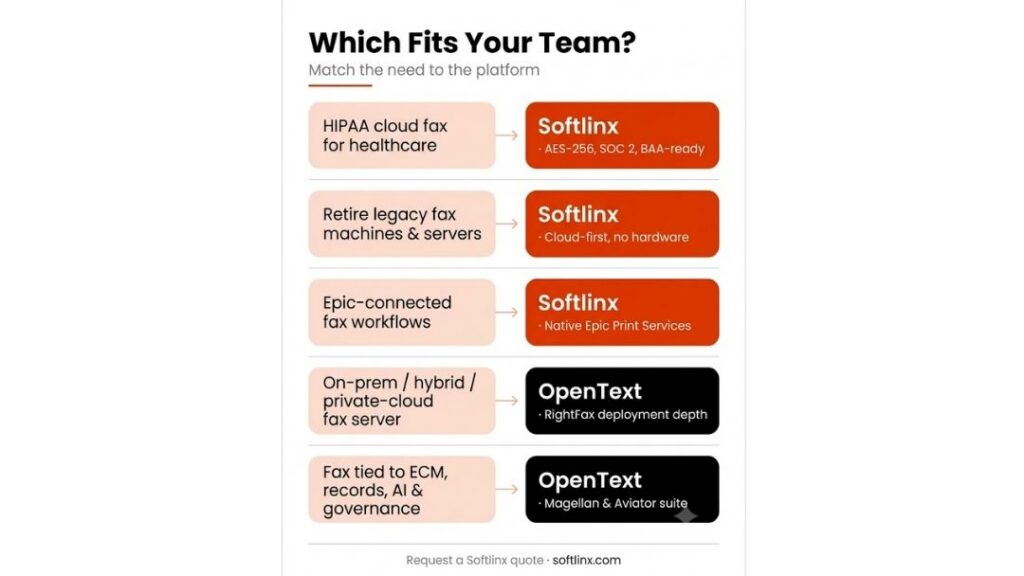
Softlinx is built for B2B cloud fax across healthcare and other regulated industries. Its ReplixFax platform supports cloud fax, web portal fax, email to fax, print to fax, production faxing, fax APIs, workflow tools, and healthcare-focused integrations. The company’s position is clear: secure document delivery for organizations that still depend on fax but need stronger control than legacy hardware can provide.
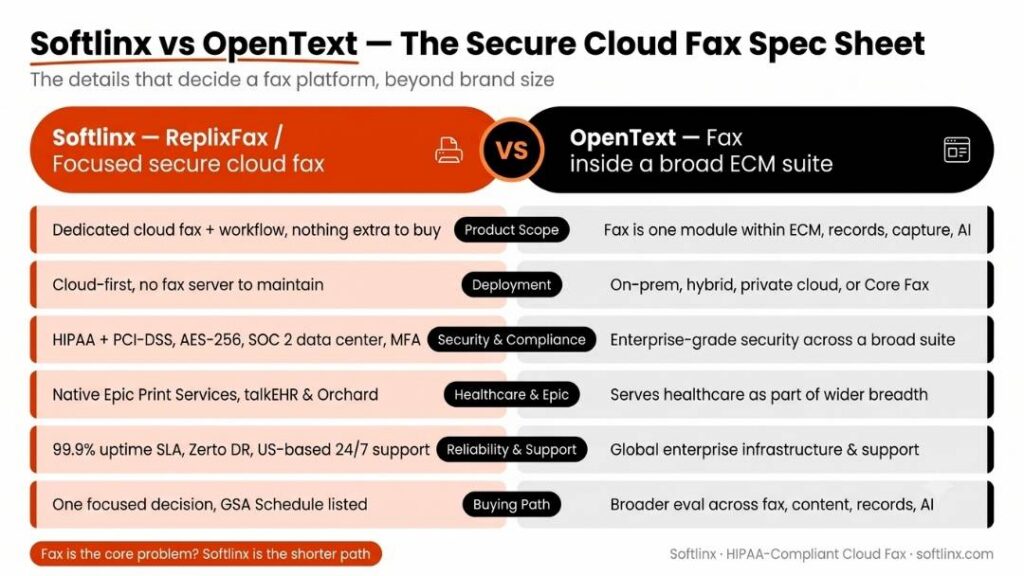
On its healthcare faxing page, Softlinx states that ReplixFax is HIPAA- and PCI-DSS-compliant, is hosted at a HIPAA-compliant SOC 2 audited data center, uses AES 256-bit encryption, supports TLS over secure communication links, offers BAA signing, provides MFA, keeps detailed audit trails, and supports user activity reports. It also references annual SOC 2 audits, penetration testing, and vulnerability testing.
Those details matter because buyers are not just looking for hipaa compliant faxing as a label. They are looking for a system that can support real departments, real users, and real document flow. A clinic may need secure inbound records. A hospital may need EHR-connected fax. A billing company may need high-volume queues. A government office may need controlled access. An insurance team may need better claim document routing.
Softlinx also supports multiple ways to send and receive fax. Teams can use a secure web portal, email-to-fax, print-to-fax, APIs, or application workflows. That flexibility matters because no two organizations handle documents in the same way.
A team that wants a broader service view can start with the Softlinx cloud fax service. Teams that still use local infrastructure can compare it with a cloud fax server alternative. Organizations that need browser-based sending can review the secure web portal fax option, while teams that prefer inbox-based workflows can look at email to fax for business accounts.
Buyer Checklist Before You Choose a Cloud Fax Provider
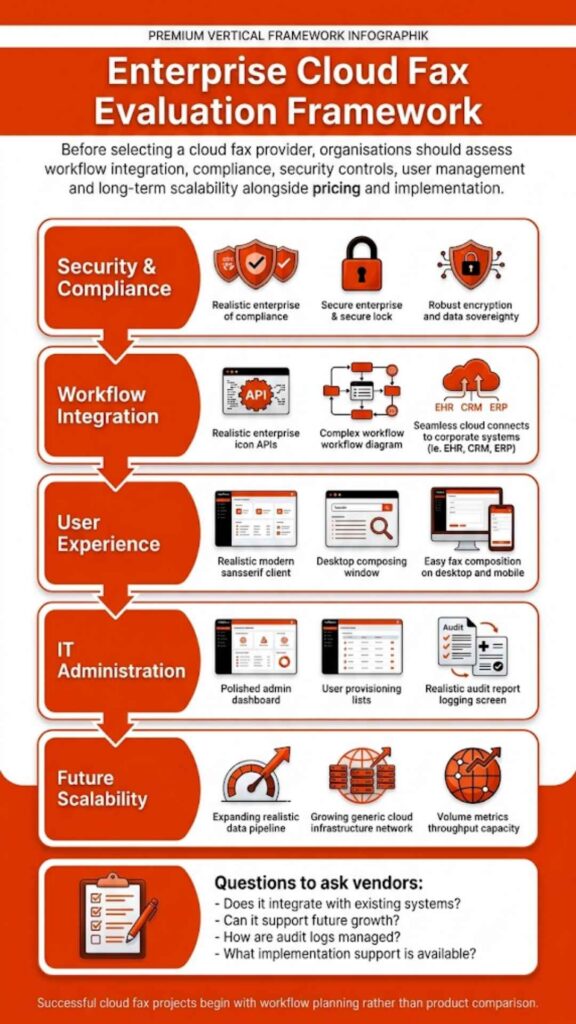
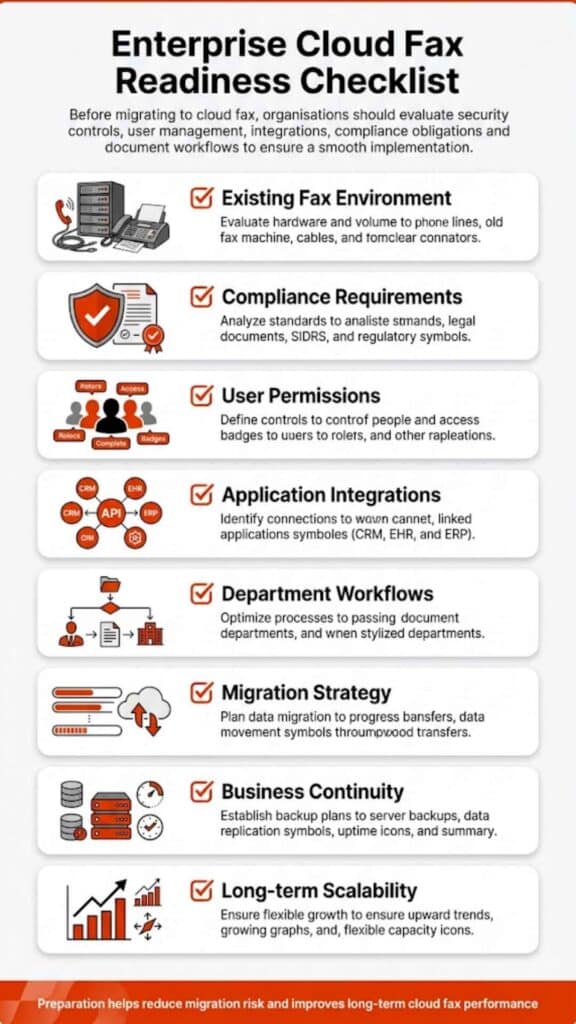
Use this checklist before signing with any cloud fax provider. It can help IT, compliance, operations, and procurement teams review the same facts instead of relying on scattered claims.
| Buyer question | Why it matters |
| Will the provider sign a BAA for healthcare use? | A BAA is essential when the provider handles ePHI for HIPAA-regulated organizations |
| Is SOC 2 Type II documentation available for review? | It gives buyers stronger evidence that controls operated over time |
| Does the platform support MFA and role-based access control? | These controls reduce weak access patterns and shared-account risk |
| Are faxes encrypted in transit and at rest? | Encryption helps protect secure document exchange across storage and transmission |
| Can administrators manage fax numbers by department or user? | Controlled number management helps reduce routing confusion |
| Are audit trails and user activity reports available? | Logs help compliance teams review who sent, viewed, routed, or changed fax activity |
| Can inbound faxes route to secure queues or applications? | Workflow routing helps keep sensitive documents away from open inboxes or printers |
| Does the provider support high-volume fax needs? | Enterprise teams need dependable queues, status visibility, and operational support |
| Are retention settings clear and configurable? | Retention control helps reduce unmanaged storage of sensitive records |
| Can the provider explain data residency and hosting? | Location and storage details may matter for regulated or contract-bound data |
FAQs About Cloud Fax Compliance Certifications
Is fax HIPAA compliant?
Fax can be part of a HIPAA-compliant process, but the full workflow matters. Healthcare organizations should use proper safeguards, verify recipients, protect PHI, control access, and work with vendors that sign a BAA when they handle ePHI.
Are faxes HIPAA compliant when sent online?
Online fax can support HIPAA-compliant faxing when the provider offers a signed BAA, encryption, access controls, audit trails, secure storage, and clear policies for PHI. A basic consumer fax app is not enough for healthcare use.
Is eFax HIPAA compliant?
The answer depends on the specific eFax service, plan, agreement, and controls. Buyers searching for is efax HIPAA compliant, efax protect, hipaa efax, or efax services HIPAA compliant should check for a signed BAA, encryption, audit logs, MFA, and business-grade security documentation.
What does HIPAA say about faxing patient information?
HIPAA does not ban faxing patient information. It requires covered entities and business associates to protect PHI through proper safeguards. When a cloud provider handles ePHI, HHS guidance says a HIPAA-compliant BAA is required.
Do I need a BAA for HIPAA online fax?
Yes, when the provider creates, receives, maintains, or transmits ePHI for a covered entity or business associate. The BAA defines the vendor’s responsibilities for safeguarding ePHI.
What is the difference between HIPAA and SOC 2 for cloud fax?
HIPAA is a healthcare privacy and security law. SOC 2 is an independent audit framework for service organization controls. A healthcare cloud fax provider may need both HIPAA support and SOC 2 evidence to satisfy compliance and vendor risk reviews.
Should a cloud fax provider have PCI DSS compliance?
PCI DSS matters when fax workflows may store, process, transmit, or affect payment account data. Financial services teams, billing departments, and insurance operations should ask how payment-related faxes are protected.
Is HITRUST required for HIPAA-compliant faxing?
HITRUST is not always required, but it can strengthen healthcare vendor assurance. If a provider does not have HITRUST, buyers should look closely at SOC 2 reports, BAAs, encryption, MFA, audit trails, testing, and risk documentation.
What security controls should a HIPAA compliant web fax include?
A HIPAA-compliant web fax should include encryption, MFA, role-based access control, audit logs, secure storage, user activity reports, administrative controls, retention settings, and a signed BAA for healthcare use.
Make Compliance Part of the Fax Buying Decision
So, what compliance certifications should a cloud fax provider have? At minimum, healthcare organizations should look for HIPAA support with a signed BAA, audited security controls such as SOC 2, encryption, MFA, role-based access control, audit trails, and industry-specific safeguards such as PCI DSS when payment data is involved. HITRUST, ISO 27001, NIST alignment, FedRAMP expectations, and data residency controls may also matter depending on the organization.
The strongest provider is not the one with the longest list of badges. It is the one that can show the right mix of certifications, legal agreements, technical safeguards, support, and workflow design.
Softlinx ReplixFax is designed for that kind of environment. It supports HIPAA-compliant cloud fax, secure document exchange, healthcare workflows, enterprise fax tools, cloud fax APIs, and regulated industry use cases without relying on unsupported pricing or savings claims.
If your team still depends on fax for PHI, claims, account records, signed forms, or high-volume document delivery, now is the right time to review where risk enters the workflow. Look at who can access each fax, how documents are routed, whether audit trails are easy to review, and whether your provider can support the compliance controls your industry expects. Then compare those needs with Softlinx’s secure cloud fax capabilities and request a cloud fax quote to see which controls fit your workflow, locations, users, and document volume.